

Cybersecurity for the Maritime sector
With more than 90% of the world’s cargo transported by sea each year, the maritime sector forms a vital link in the global economy. And as the industry embraces digital technologies by integrating IoT technologies, connecting IT and OT systems, and exploring autonomous capabilities, it becomes a bigger target for cyber attacks.[1]
Dutch maritime organizations are at the forefront of this technological evolution. Since the 1980s, the Netherlands has invested heavily in maritime R&D, becoming a global leader in smart shipping and high-tech port infrastructure. But this leadership brings exposure. Threat actors from China, Russia and Iran are well known to target the maritime sector to obtain commercial and/or intellectual advantages, while the Port of Rotterdam lies in the crosshairs of geopolitical conflicts due to its strategic and economic importance.[2][3]
How can you address this growing threat?
There is this legendary saying on how to overcome your adversaries: 'know thy enemy and know yourself; in a hundred battles, you will never be defeated'. This starts with gaining an understanding of your threat landscape, your adversaries’ intentions, their modus operandi, and specific attacking methods. This page outlines the key threats facing the maritime sector today, along with effective methods for defending against them.
Request a free membership to access our full research insights
Already a member? Login here
Threat landscape
For the maritime industry
Advanced Persistent Threats (APTs)
Tactics, Techniques & Procedures (TTPs)
Attack tools
| Maritime | Maritime + related | Broader focus | All known | |
|---|---|---|---|---|
| APTs | 94 | 121 | 512 | 801 |
| TTPs | 1,674 | 2,123 | 3,541 | 4,112 |
| Attack tools | 1,474 | 1,821 | 3,027 | 3,666 |
Maritime faces more cyber threats than ever
To stay in control becomes more difficult
Data from Hunt & Hackett’s proprietary Threat Diagnostic System shows an increase in cyberattacks targeting the maritime sector in recent years, and the stakes are high: the port of Rotterdam alone accounts for 6.2 percent of the Dutch economy. Across the EU, 7.5 percent of all incidents between July 2024 and June 2025 were directed against transport infrastructure. In particular, state-sponsored Advanced Persistent Threats (APTs) target maritime organizations to gain access to critical technologies, intellectual property, and sensitive operational data. These attacks are often part of broader geopolitical strategies, aimed at gaining long-term economic and strategic advantages.
At the same time, the sector’s pivotal role in global trade makes it an appealing target for financially motivated threat actors. Ransomware groups and cybercriminals understand that even short-lived disruptions to port operations or shipping schedules can have massive financial consequences, making maritime organizations particularly vulnerable to extortion-based attacks. Adding to this, hacktivists and other politically motivated actors have turned their attention to the sector in recent years, seeking to disrupt maritime operations to send a political message. Together, these threats not only jeopardize the continuity of global trade but also pose serious risks to the safety of crews at sea.[4][9][10][11][12][13]
Actor overview
The most active attack groups targeting the maritime sector are shown in the dynamic chart below. This highlights the relationships between the various threat actors, their motivation and their country of origin.
Knowing the APT groups, their motivations and origin countries provides a solid starting point for understanding what you are up against. To get a more comprehensive understanding of the threat landscape, it is important to research, map, and document your adversaries’ intentions to their modus operandi, attack methods and attack tools, as this provides more actionable information for strengthening your defences.
More detailed information on the threat landscape for this sector?
Already a member? Login here
How it works
Threat landscape for the maritime sector
Attacks in the maritime sector
Look down! Look out! Look up!
The following section explores a few selected cyberattacks in the maritime sector in greater detail. These cases highlight the diverse range of threats affecting the industry across multiple countries and sub-sectors. However, they represent only a small fraction of the cyberattacks occurring daily.
October 1, 2024
12:00 PM
Mustang Panda espionage against EU organizations
2025
Chinese state-linked hackers are running sustained espionage campaigns against maritime organizations across Europe. The EU's cybersecurity agency ENISA singled out Mustang Panda (also known as Earth Preta) as the most prominent group in shipping, with continuous campaigns against maritime-related organizations in at least seven EU member states. The group uses spear-phishing, compromised USB drives and a range of malware, including customized versions of the PlugX remote-access tool. Cargo shipping companies in Norway, Greece and the Netherlands are among the reported targets.
ENISA did not name the seven states or the companies breached, and has not said whether the 2025 campaigns are continuing. The activity was aimed mainly at espionage and strategic intelligence collection rather than immediate disruption. That makes it easy to miss: a shipping company can be compromised for long periods without any visible operational impact.[13][17][12]
October 1, 2024
12:00 PM
DDoS attacks on Dutch ports
2023
In June 2023, the websites of major Dutch ports, including Groningen, Amsterdam, Rotterdam, and Den Helder, were taken offline by coordinated Distributed Denial of Service (DDoS) attacks. Claimed by the pro-Russian hacktivist group NoName057(16), the attacks were retaliation against the Netherlands' decision to purchase Swiss tanks for Ukraine as part of the ongoing Russia-Ukraine conflict. The websites were primarily used as a means of informing the public, rather than for port operations, so the impact was negligible. Nonetheless, this incident shows how maritime infrastructure can become caught in the crosshairs of geopolitical conflicts.[38]
October 1, 2024
12:00 PM
Royal Dirkzwager ransomware
2023
In March 2023, Dutch maritime logistics company Royal Dirkzwager suffered an attack by Play ransomware group. The attackers encrypted company systems and exfiltrated sensitive customer data, including email addresses and personal information. Although the ransomware caused minimal operational disruption, the stolen data provided significant leverage for ransom negotiations. Royal Dirkzwager, who supports more than 800 maritime organizations with critical logistical information, publicly apologized for the breach and subsequently implemented enhanced security measures, including Endpoint Detection and Response (EDR) software, to prevent future incidents.[40]
October 1, 2024
12:00 PM
Oiltanking/Mabanaft/EVOS oil terminal ransomware
2022
In 2022, a ransomware attack disrupted oil terminals in ports in the Netherlands, Belgium and Hamburg, Germany. Six oil storage terminals in the Amsterdam-Rotterdam-Antwerp refining hub had difficulty loading and unloading refined product cargoes, according to news reports. Terminals could not process barges, which made it impossible for tankers to deliver or unload, and fuel supplies had to be rerouted. German security services reportedly believe the attack began with BlackCat ransomware, as first reported by the German newspaper Handelsblatt; this is a media-reported assessment rather than a formal attribution.
The case shows how a single ransomware campaign can hit several terminals in different countries at once, and how quickly trouble at storage terminals turns into a fuel logistics problem for the whole region.[22][23][16][24]
October 1, 2024
12:00 PM
Stena Impero seizure
2019
In July 2019, a UK-flagged product tanker called the Stena Impero was seized by Iranian forces in the Strait of Hormuz after allegedly veering into Iranian waters. Investigations later indicated the vessel's Automatic Identification System (AIS) - used to track ship positions and movements - may have been spoofed, a technique used to manipulate the GPS capabilities of vessels. The incident occurred just 15 days after the British Navy detained the Iranian tanker Grace 1 near Gibraltar and was widely seen as retaliation. While Iran denied tampering with the AIS, this case shows how GPS interference can be used by states to gain geopolitical leverage against their adversaries. Given the fact that AIS spoofing is a relatively low-tech, inexpensive endeavor, it is likely that this tactic will only grow in popularity, particularly as global tensions heighten.[41]
October 1, 2024
12:00 PM
Maersk Not Petya
2017
In 2017, shipping giant Maersk suffered one of the most significant cyber incidents ever to hit the maritime industry. The NotPetya attack, which initially targeted Ukrainian entities, spread globally through compromised software, claiming victims in more than 60 countries. Maersk was among the hardest hit, losing an enormous chunk of its IT infrastructure thanks to the wiper malware’s destructive capabilities. In fact, the company reported the loss of over 49,000 end-user devices and 1,000 business applications, resulting in damages exceeding $300 million. The attack was eventually attributed to the Russian APT Sandworm, who were working to sabotage and disrupt key Ukrainian entities due to geopolitical tensions between Russia and Ukraine. It appeared that Maersk – like the vast majority of NotPetya's victims – was simply collateral damage. Nonetheless, the impact of this incident was enormous, highlighting the vulnerability of even the industry’s largest, most well-resourced players.[42]
Key Trends
For the maratime sector
The maritime sector is becoming more vulnerable to cyber threats due to several industry-wide trends. Leading the way is a growing reliance on digital technologies, which significantly expands the attack surface. At the same time, aging operational technology and increased IT-OT interconnectivity are introducing new risks. In this section, we take a closer look at the most important trends shaping the threat landscape.
Geopolitical tension turns Dutch and European ports into targets of hybrid pressure
Dutch ports have been caught in the crosshairs of pro-Russia hacktivist attacks conducted in retaliation for military or diplomatic support given to Ukraine. In the EU's 2025 threat landscape for transport and ports, nearly 88% of incidents were hacktivist-driven DDoS attacks, often timed with political events.[31][5]
The pressure goes beyond disruption. Dutch intelligence services assess that Russia is carrying out cyber operations against Dutch public institutions, critical infrastructure and laying the groundwork for sabotage. They also warn that Russia is mapping seabed infrastructure and conducting maritime espionage – which could later support sabotage - and that Europe has seen a sharp rise in such activity since late 2023. Ports are exposed because most are commercially operated yet serve military logistics functions, which makes them attractive hybrid-warfare targets.[14][16]
Shared software vendors and long supply chains concentrate risk
The supply chain is the most sensitive target in the maritime ecosystem, because port operations alone can involve hundreds or thousands of companies. An incident at one party can have consequences for the entire chain. Small and medium-sized companies in particular often lack the resources or knowledge to protect themselves. In the Netherlands, growing dependence on a few software suppliers is a recognized risk, since technical or human errors have already caused major disruptions. The Port of Rotterdam Authority also warns against excessive reliance on American cloud providers.[10][33][34][35]
Vendors that serve ports and carriers often hold years of support correspondence, EDI configurations, billing data and user lists, so one compromised support environment can expose many customers whose own networks were never touched. On ships, remote vendor access is consistently identified as the largest practical exposure: engine makers, ECDIS suppliers and automation vendors connect for diagnostics, often through arrangements nobody in the shipowner's organization has documented.[30][36]
Connectivity and IT/OT convergence widen the attack surface
Operational Technology (OT) systems, which control crucial physical processes aboard ships and within ports - such as propulsion systems, cargo handling, and navigation - have emerged as attractive targets for cyber attackers. Between 2017 and 2020 alone, cyberattacks on maritime OT systems skyrocketed by 900%, and these attacks have only become more prevalent in the years since.
One of the biggest challenges in securing maritime OT environments is the longevity and diversity of ship equipment. Typically, vessels remain operational for 25-35 years, and updates are done on different pieces of equipment at varying time intervals. Consequently, many OT systems remain unpatched and vulnerable, having been designed in an era when cybersecurity was not a primary concern.
Adding complexity, the maritime sector is rapidly adopting Internet of Things (IoT) technologies to enhance connectivity and collect real-time operational data. Such developments are essential for innovations such as autonomous shipping. However, this increasing digital interconnectivity inadvertently bridges IT and OT networks, amplifying security risks and expanding the potential attack surface.
Complicating matters, maritime operators often face a limited understanding and oversight of their full network and device inventory across fleets and operations. This lack of visibility can lead to hidden vulnerabilities, creating ideal conditions for threat actors seeking to exploit operational weaknesses and disrupt critical maritime functions.[34][43]
Incident volumes are climbing, with data extortion and ransomware at the center
Recorded attacks on shipping rose from 10 in 2021 to at least 64 in 2024 in research by a Dutch university of applied sciences, and recorded maritime cyber incidents jumped 103% during 2025, with infected USB devices among the main routes for introducing remote-access malware onto bridge systems. In the EU's 2026 threat landscape, transport accounted for 8% of all recorded cyber events, and water transport for 16.4% of transport-sector incidents.[4][13]
Ransomware is less frequent than hacktivist DDoS but remains the most damaging in downtime and cost, and criminals increasingly threaten to publish sensitive data when victims refuse to pay. In the Netherlands, more than 170 ransomware attacks took place in 2023, a considerable share against mid-sized companies. Worldwide, ransomware incidents affecting industrial entities rose to 1,211 in the fourth quarter of 2025, up from 742 in the third, and those affecting transportation organizations rose from 36 to 120 over the same period.[34][5][9]
Maturity gaps persist while the sector builds collective defenses
Maritime is still viewed as a relatively immature sector for cybersecurity, and it has been placed in the risk zone of the EU's NIS360 review for below-average cyber maturity. Some operators run mature programs, but many struggle to keep pace, mainly because new IT and OT technologies have been layered onto legacy infrastructure without comprehensive asset inventories. Recovery is also slower than often assumed.[15][12][4][11]
The sector is responding collectively. Dutch seaport operators, the Ministry of Infrastructure and Water Management and the NCTV have agreed a joint approach in the Cyber Strategy for Dutch Seaports, and updated IACS cyber requirements for ships (UR E26 and E27) apply to new ships contracted for construction from 1 July 2024. Access to threat information remains uneven, however: at the Port of Rotterdam only a handful of companies are designated as vital by the government, and only those have access to it, which the port authority considers worrying given rising digital connectedness.[2][37][35]
NIS2 compliance
For essential and important entities
Since 15 August 2026, the Dutch Cyberbeveiligingswet (Cbw) has been in force, implementing the European NIS2 Directive into national law. The legislation introduces cybersecurity obligations for essential and important entities in the maritime sector, including certain shipping companies, port authorities and operators of maritime transport infrastructure.
Organisations within its scope must comply with three core obligations: registration, cybersecurity risk management and incident reporting. Key requirements include:
- Risk assessments and appropriate security measures to protect network and information systems
- Incident detection, response and business continuity arrangements to minimise disruptions to maritime operations
- Supply chain security and vulnerability management
- Policies for assessing the effectiveness of cybersecurity measures
- Management accountability and oversight of cybersecurity risks
- Reporting significant incidents within the legally required timeframes, including an early warning within 24 hours and an incident notification within 72 hours
Hunt & Hackett's Managed Detection and Response (MDR) service supports several of these requirements through continuous security monitoring, threat detection and incident investigation. Our analysts help maritime organisations identify suspicious activity, assess potential disruptions to operations and gather the technical information needed to support regulatory reporting.
We have also developed a practical assessment framework that maps NIS2 requirements against established cybersecurity standards, including ISO/IEC 27001:2022, ISO/IEC 27002:2022 and CIS Controls. This helps maritime organisations assess their existing security measures, identify gaps and prioritise improvements in line with their obligations under the Cyberbeveiligingswet.
How to defend yourself
Threat model approach
To defend against this threat landscape, it is equally important to gain critical insights into the current resilience level of your organization. To understand thyself it is useful to let (third-party) security specialists assess your defenses and simulate meaningful attacks. When done right, such an approach provides critical insights into the resilience level of the organization against its threat landscape. Hunt & Hackett use its proprietary threat modelling-based approach with its clients in the manufacturing sector to provide meaningful insights as well as tailored solutions for the strategic, tactical, and operational aspects of their cybersecurity program.
Our approach
Controlling your cybersecurity risks
In their fight against cyber attacks, our customers typically go through several stages of maturity. By ramping up their prevention, detection and incident readiness over time – and optimizing this for their actual threat landscape – they reach a point where they have developed solid resilience against targeted attacks, with only highly controlled and accepted risks remaining.
There is no simple 'fix' to become resilient against the sophisticated cyber threats of today. Without serious resources or processes for systematic security activities, protection against modern cyber threats like ransomware is just a wish. Hunt & Hackett has developed a unique threat- and sector-driven approach to cybersecurity, enabling you to work from your current situation to a highly improved and controlled situation, optimized for your specific threat landscape and context as an organisation.
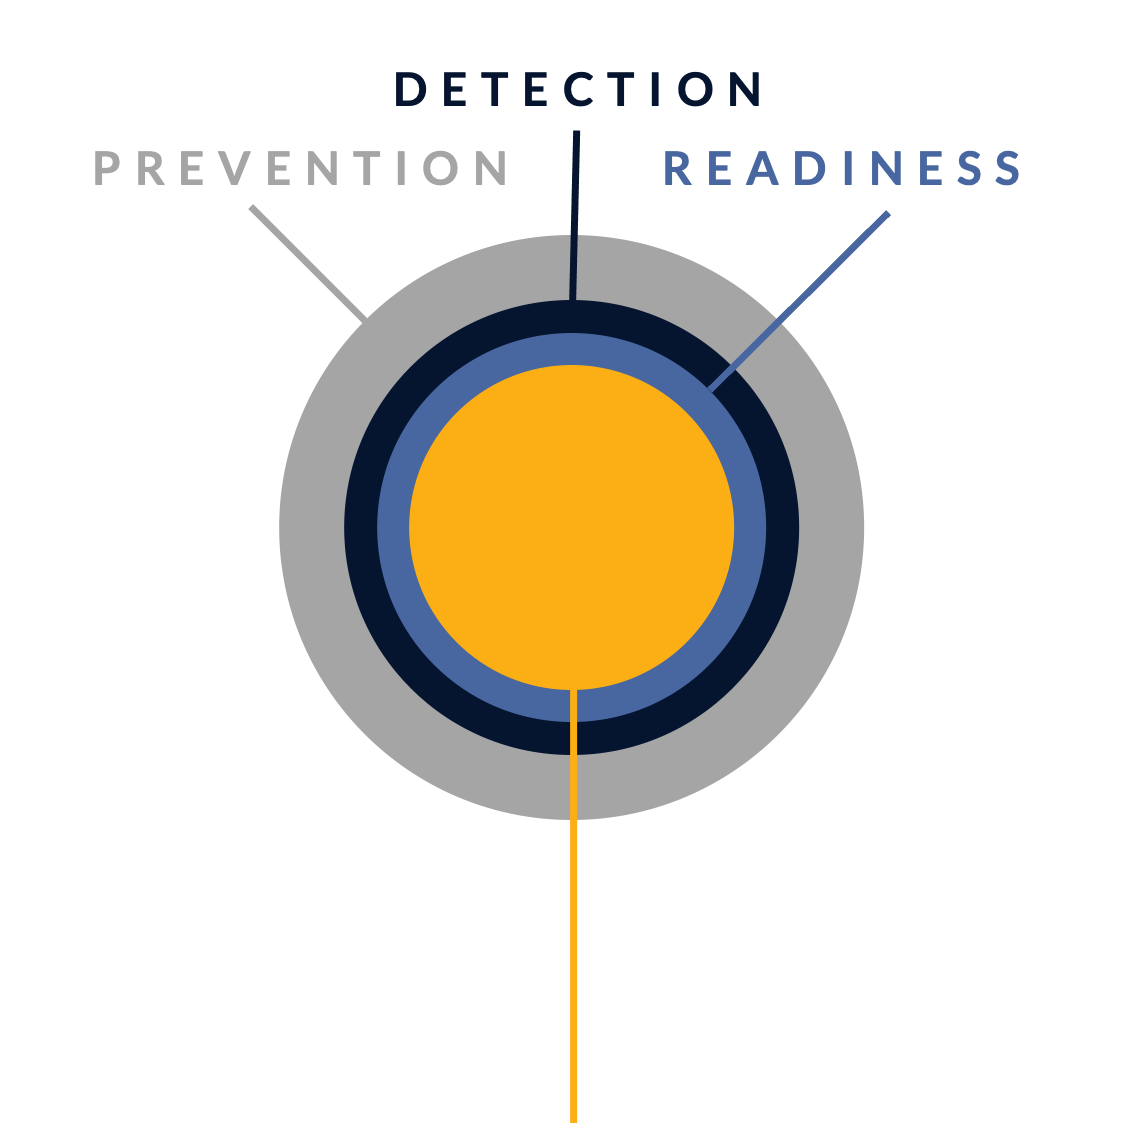
STAGE 1: Unknown risk
Pre-monitoring
-
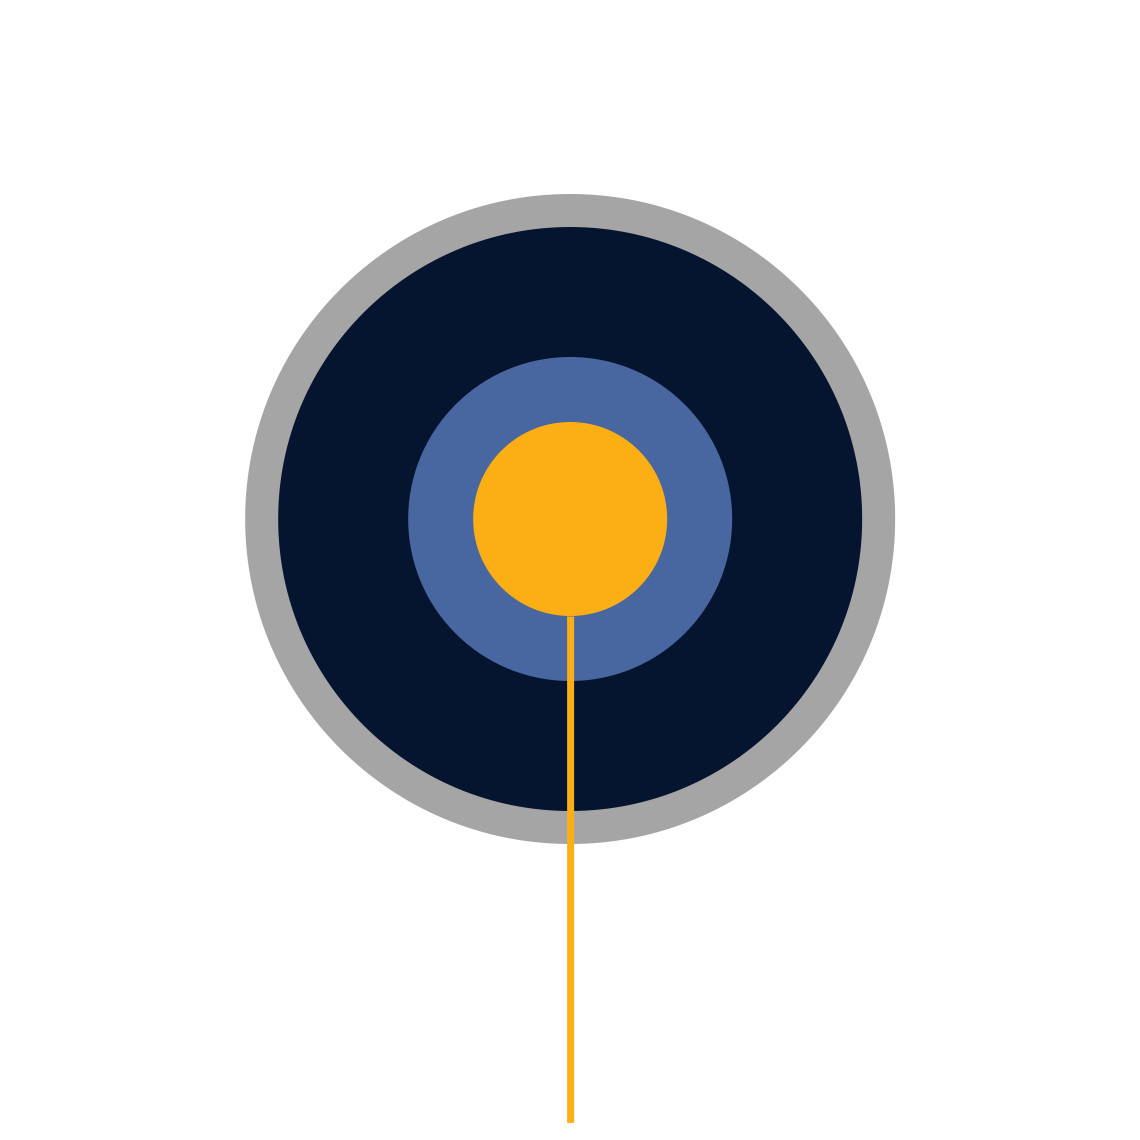
STAGE 2: Reduced risk
Post-monitoring
-
Detection & response controls
Resilience against non-targeted attacks

STAGE 3: Controlled risk
Implemented roadmap
-
Resilience against non-targeted and semi-targeted attacks
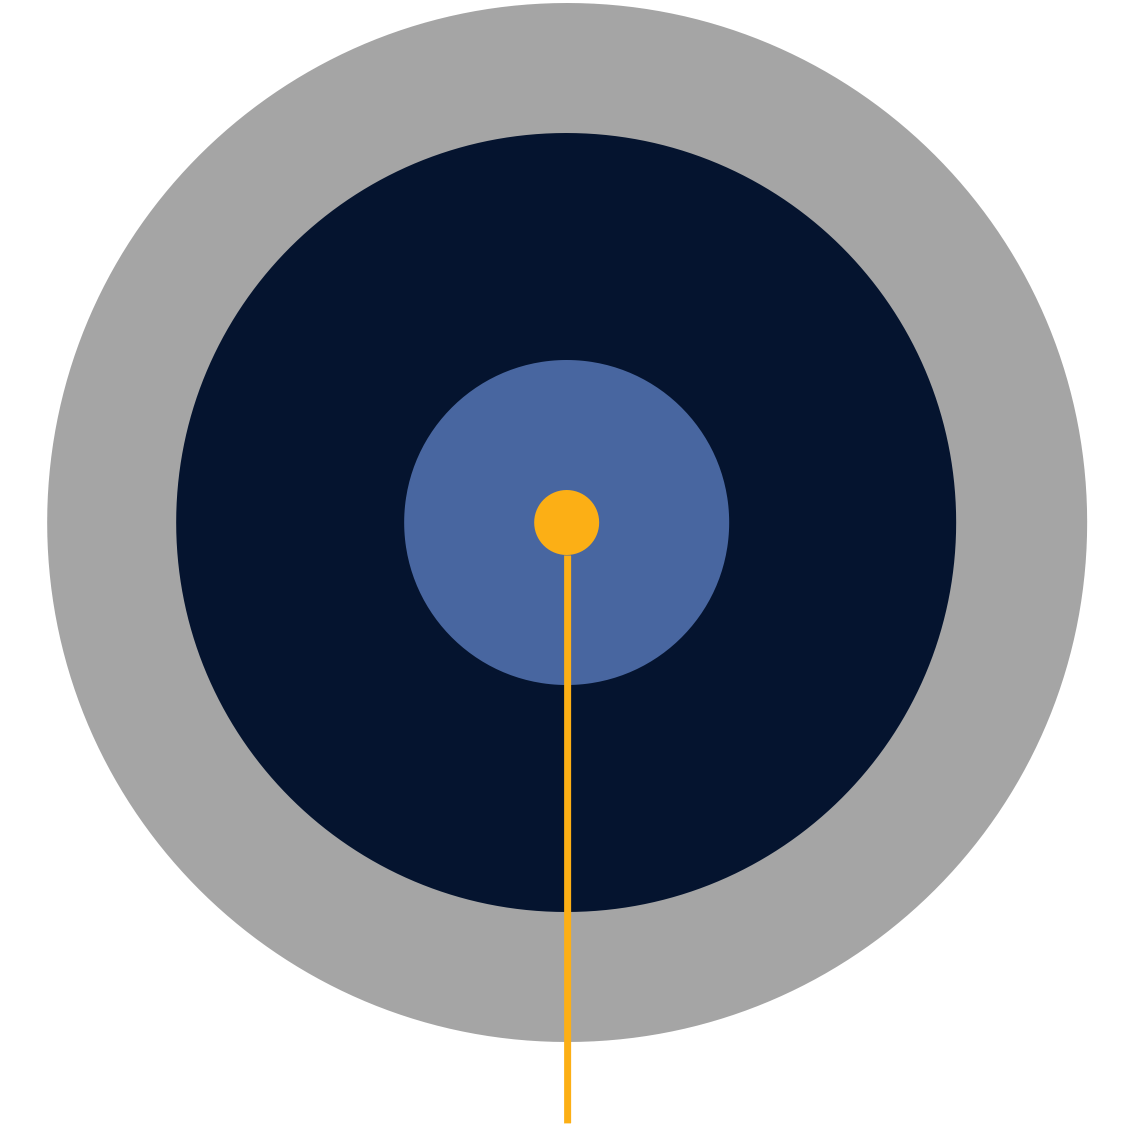
STAGE 4: Highly controlled risk
Targeted attack resilience
-
Our services
Optimized for the maritime industry
Because we use your actual threat landscape and your sector as our starting points, our services are optimised for your specific context and needs.
Managed Detection & Response (MDR)
We detect & react to attacker activity in your environment, minimizing the impact on your business.
Security Program Gap Assessment (SPGA)
We assess your current security program, threat landscape, security controls and risk.
Incident Response (IR)
We help you manage a cyber crisis and contain security incidents, breaches and cyber threats.
Breach & Attack Simulation (BAS)
We validate your security choices by simulating attacks.
Our articles about the maritime sector
From Hunt & Hackett experts
References
[1] https://maritiemland.nl/nieuws/onderzoekers-nhl-stenden-brengen-met-database-maritieme-cyberaanvallen-in-kaart/
[2] https://maritiemland.nl/nieuws/nederlandse-zeehavens-en-ferm-lanceren-landelijk-cybersecurity-platform/
[3] https://www.enisa.europa.eu/topics/cybersecurity-of-critical-sectors/transport
[4] https://breakbulk.com/articles/ports-under-siege
[5] https://feport.eu/news/enisa-threat-landscape-2025-highlights-cyber-risks-for-transport-and-ports-lisbon/
[6] https://www.ncsc.nl/ondernemersverhalen/gevaar-op-zee-na-hack-bij-maritieme-dienstverlener
[7] https://www.rotterdammaritimecapital.com/news/the-need-for-cyber-resilience-in-mainport-rotterdam
[8] https://www.hklaw.com/en/insights/publications/2026/10/recent-cyber-incidents-underscore-the-need-for-maritime-cybersecurity
[9] https://www.dragos.com/blog/dragos-industrial-ransomware-analysis-q4-2025
[10] https://www.enisa.europa.eu/news/maritime-sector-sails-through-rough-cybersecurity-seas
[11] https://www.vno-ncw.nl/forum/elk-jaar-een-grote-ramp-zo-blijft-de-rotterdamse-haven-weerbaar
[12] https://www.sofx.com/china-linked-hackers-spied-on-shipping-in-seven-eu-states/
[13] https://splash247.com/china-linked-hackers-step-up-attacks-on-european-shipping/
[14] https://therecord.media/russia-cyberattacks-europe-warfare
[15] https://www.computable.nl/2026/06/26/alle-hens-aan-cybersecurity-dek/
[16] https://www.helpnetsecurity.com/2025/07/23/ccdcoe-maritime-port-cyber-attacks/
[17] https://cyble.com/blog/cyberattacks-targets-maritime-industry/
[18] https://nltimes.nl/2023/06/14/dutch-ports-websites-offline-hours-days-due-pro-russian-cyber-attacks
[19] https://gcaptain.com/pro-russian-hackers-target-website-of-europes-busiest-port/
[20] https://therecord.media/prorussian-hackers-claim-attacks
[21] https://therecord.media/royal-dirkzwager-ransomware-attack-dutch-shipping
[22] https://maritimecybersecurity.nl/incident/N0r68rPzb3
[23] https://www.bankinfosecurity.com/cyberattack-cripples-european-oil-port-terminals-a-18465
[24] https://maritime-executive.com/article/cyberattack-disrupting-northern-european-oil-hubs-in-major-ports
[25] https://maritimecybersecurity.nl/incident/MyKmGWmYW1
[26] https://jjoerlemans.com/2026/03/10/veroordelingen-en-modus-operandi-hack-in-de-haven-van-rotterdam-en-antwerpen/
[27] https://www.infosecurity-magazine.com/news/anubis-ransomware-adriatic-port/
[28] https://theloadstar.com/cyber-crime-group-hits-38-shipping-and-port-groups-with-date-leak-threat/
[29] https://www.nt.nl/voorpagina/2026/10/15/nederlands-kantoor-premier-alliance-genoemd-bij-dreiging-met-datalek-bij-38-bedrijven/
[30] https://cydome.io/n0n-cyber-extortion-incident-involving-38-maritime-companies-likely-traces-back-to-a-single-vendor/
[31] https://securityaffairs.com/177312/hacktivism/pro-russia-hacktivist-group-noname05716-is-targeting-dutch-organizations.html
[32] https://www.dragos.com/resources/press-release/dragos-2026-year-in-review-new-ot-threats-ransomware
[33] https://www.dinalog.nl/en/project/cyber-security-in-the-rotterdam-maritime-sector
[34] https://www.maritiemmedia.nl/nieuws/scheepvaart/18225/cybersecuritybeeld-nederland-2024-voor-ondernemers
[35] https://maritiemland.nl/nieuws/havenbedrijf-rotterdam-bezorgd-over-cyberdreiging/
[36] https://zeaclub.com/resources/zea-notes/maritime-cyber-security/
[37] https://iacs.org.uk/news/iacs-ur-e26-and-e27-press-release
[38] https://nltimes.nl/2023/06/14/dutch-ports-websites-offline-hours-days-due-pro-russian-cyber-attacks
[39] https://therecord.media/royal-dirkzwager-ransomware-attack-dutch-shipping
[40] https://dirkzwager.com/news/cyber-security-update/
[41] https://www.seatrade-maritime.com/crewing/stena-impero-released-by-iran
[42] https://www.1kosmos.com/resources/security-glossary/notpetya
[43] https://safety4sea.com/cyber-attacks-on-maritime-ot-systems-increased-900-in-last-three-years/