

Cybersecurity for the Logistics sector
Over the past few years Hunt & Hackett has observed a discerning increase in the activity of Advanced Persistent Threat (APT) groups in the logistics sector. Logistics has long been the backbone of global trade, seamlessly connecting economies and ensuring the smooth flow of goods. But as the industry rapidly digitizes, it has become an increasingly attractive target for cyber threats.
One might not immediately assume that the logistics industry is a valuable target; after all, financial institutions have the money and government entities have the information hackers desire, right? Not quite. In fact, logistics companies manage vast amounts of sensitive data, and private and public entities depend on their operations every single day. These factors make them highly vulnerable to attacks.
How can you address this growing threat?
There is this legendary quote from Sun Tzu on how to overcome your adversaries: 'know thy enemy and know yourself; in a hundred battles, you will never be defeated'. To know your enemy starts with gaining an understanding of yourself, your threat landscape, your adversaries’ intentions, their modus operandi, and specific attacking methods. On this page, the cyber threats to the logistics sector are explored. Understanding the full picture of the challenges our clients may encounter helps us in doing what we do best: ensuring security for your business from specific cyber threats targeting your organization.
Request a free membership to access our full research insights
Already a member? Login here
Threat landscape
For the logistics industry
Advanced Persistent Threats (APTs)
Tactics, Techniques & Procedures (TTPs)
Attack tools
| Logistics | Logistics + related | Broader focus | All known | |
|---|---|---|---|---|
| APTs | 94 | 136 | 193 | 781 |
| TTPs | 1,674 | 1,998 | 2,458 | 4,109 |
| Attack tools | 1,474 | 1,577 | 1,996 | 3,616 |
Logistics faces more cyber threats than ever
To stay in control becomes increasingly difficult
Our proprietary threat diagnostic system shows a discernible increase in malicious activity targeting the logistics sector. As logistics companies race to keep up with rising global demand amid supply chain disruptions, cybercriminals are taking advantage of the pressure. If you operate in the sector, the risks of cyber-attacks, including intellectual property (IP) theft, ransomware, data breaches, and espionage, are escalating, especially if the appropriate defenses are not in place.
Cyber risk is widely recognized in Dutch transport and logistics. In May 2025 research, 80 percent of Dutch transport entrepreneurs said cybercrime is a risk to their organization, and 16 percent had suffered financial damage from cyber incidents. Across the EU, transport ranked second among targeted sectors, with 7.5 percent of all incidents between July 2024 and June 2025, and logistics is the second most impacted transport subsector after aviation. State-linked activity is a factor too: globally, transport and logistics organizations featured in 8 of 14 observed APT campaigns (57 percent) in the latest reporting period, up from 6 of 16 (38 percent) in the period before.[1][2][3][4]
This pressure has several causes. First, logistics is easy to extort. The sector works with tight schedules and short lead times, leaving little room to absorb an outage. Paying a ransom is therefore tempting, and criminals know it. The chain of carriers, distribution centers, service providers and authorities adds to the exposure: a well-secured head office can still be hit through a supplier or partner, and compromising one link can unlock the data or operations of many organizations. Many transport and logistics companies are also small and medium-sized enterprises with small IT departments and infrequent company-wide updates, so comparatively low effort can cause a great deal of damage. Stolen credentials for freight platforms also enable fraud and cargo diversion. Second, logistics providers hold information that others want. Breaking into their systems gives criminals access to information on routes and goods that customers have entrusted to them. Russian military intelligence (GRU unit 26165) widened its targeting of logistics entities and technology companies involved in delivering aid to Ukraine, and pursued accounts holding sensitive shipment information such as train schedules and shipping manifests.[5][6][7][8][9][10][11][12]
And third, transport systems count as critical infrastructure, which makes them a frequent target of both politically and financially motivated threats. Ports show this clearly. Rotterdam's port alone accounts for 8.2 percent of Dutch GDP, and companies there are interesting to geopolitical actors as well as to criminals after money, because an attack on a port has a great deal of impact. Most ports are commercially operated yet serve military logistics functions, which makes them attractive hybrid warfare targets, and port infrastructure, responsible for 80 percent of global trade, is increasingly under attack by actors tied to Russia, Iran and China. Pro-Russian hacktivists, for their part, often single out logistics companies in NATO member states.[1][13][14][15]
Actor overview
The most active attack groups targeting the logistics sector are shown in the dynamic chart highlighting the relationships between the various threat actors, their motivation and their country of origin.
Knowing the APT groups, their motivations and origin countries provides a solid starting point for understanding what you are up against. To get a more comprehensive understanding of the threat landscape, it is important to research, map, and document your adversaries’ intentions to their modus operandi, attack methods and attack tools, as this provides more actionable information for strenghtening your defences.
More detailed information on the threat landscape for this sector?
Already a member? Login here
How it works
Threat landscape for the logistics sector
Attacks in the logistics sector
Look down! Look out! Look up!
The following section explores a few selected cyberattacks in the logistics sector in greater detail. These cases highlight the diverse range of cyber threats affecting the industry across multiple countries and subsectors, with varying tools and impacts. However, they represent only a small fraction of the cyberattacks occurring daily.
January 1, 2026
16:00 PM
CEVA Logistics breach
2026
In 2026, Ceva Logistics, one of the world's largest shipping and logistics companies, was hacked. Operations at eight of its warehouses in Europe were reportedly disrupted over a weekend, delaying shipments for retail customers whose inventory was stored there. Several client companies said their own personal information was also stolen. Affected companies reportedly include Dutch e-commerce company Bol, department store De Bijenkorf, eyewear company Ace & Tate, football club Ajax and Steam's hardware business in Europe. Ceva operates eight e-commerce locations in the Netherlands and names Bol, Zalando and De Bijenkorf among the customers it serves there.
Bol said unauthorized parties gained access to two systems used to process orders from one of its distribution centers, that none of its own systems were affected, and that customer data processed there may have been accessed or copied. Potentially exposed data includes names, addresses, phone numbers, email addresses, order numbers, tracking information and purchase details. The Dutch data protection authority received breach reports from 10 organizations in relation to the incident. There is no public attribution, and it remains unclear whether ransomware was deployed or an extortion demand was made.[16][17][18]
January 1, 2026
16:00 PM
Ahold Delhaize / Albert Heijn cyberattack
2026
In 2026, Ahold Delhaize, the group behind Dutch supermarket chain Albert Heijn, detected suspicious activity in its IT infrastructure, brought in cybersecurity experts, and confirmed that the activity resulted from malicious actions by others. The company's response affected most of its brands across Europe and the United States, to varying degrees, although stores stayed open throughout. Industry experts estimate the incident cost Albert Heijn at least €10 million.
The company notified the Dutch National Cyber Security Centre (NCSC) within 24 hours of discovering the activity and kept the NCSC, law enforcement and other authorities updated. In its update of October 19, it did not identify those responsible or disclose technical details, so the attacker and the method remain unknown. [19][20]
January 1, 2026
16:00 PM
Dutch haulage and logistics ransomware cases
2024-2026
Dutch haulage and logistics providers have faced a steady run of ransomware. Road haulier AB Texel was hit by a ransomware attack on February 16, 2024. The company said service and operations continued, started a recovery operation immediately, filed a police report and notified the Dutch Data Protection Authority. On November 15, 2024, Klarenbeek Transport discovered it had been attacked by the BlackSuit group, which stole essential data and encrypted key files, threatening business operations and customer data. Six days later, on November 21, 2024, the logistics systems of Jumbo and Hema, which run on Blue Yonder software, were hit by ransomware. Backup systems absorbed the blow, and the software was temporarily taken out of service. [21][1]
January 1, 2023
16:00 PM
Royal Dirkzwager (Play ransomware)
2023
In 2023, Royal Dirkzwager, a Dutch maritime logistics company founded in 1872, was hit by ransomware from the Play group. The company provides information to more than 800 maritime organizations and registers more than 200,000 ship movements a year, and its systems tell ports when ships will arrive and which nautical services will be available. The attackers leaked a 5 GB archive as proof and threatened to publish the full data set if the ransom was not paid. The Dutch Data Protection Authority was notified, and the company said it was negotiating with the criminals. Systems were running again six days later, but the cleanup took far longer, despite the negotiations. [22][23][5]
January 1, 2023
16:00 PM
NoName057(16) DDoS on Dutch port websites
2023
In 2023, pro-Russian hackers knocked the websites of several Dutch ports offline for hours to days. The port companies of Eemshaven and Delfzijl, Amsterdam, Rotterdam and Den Helder confirmed they were hit by DDoS attacks. The Port of Rotterdam said the damage did not go beyond its website and that shipping systems were not affected. The group NoName057(16), which mostly uses a DDoS toolkit called DDoSia, hinted that the attacks were a response to the Dutch plan to buy Swiss tanks for Ukraine.
The group's members often target banks, private companies supplying the defense industry and logistics companies in NATO member states. In a separate law-enforcement action on July 15, a botnet of hundreds of computer systems worldwide was shut down and seven arrest warrants were issued, including against the main instigators living in the Russian Federation. [15][24][25]
January 1, 2022
16:00 PM
Russian GRU unit 26165 (APT28) campaign against Western logistics entities and IP cameras on military routes
2022-2026
For more than two years, Russia's GRU military unit 26165, known as APT28 or Fancy Bear, ran an espionage-oriented campaign against Western logistics providers and technology companies, including those involved in coordinating, transporting and delivering aid to Ukraine. The unit widened its targeting of these companies as Russian forces missed their military objectives and Western countries supported Ukraine's defense. Dozens of government and commercial entities were targeted across air, sea and rail. The actors used known techniques: password spraying, spearphishing and changes to Microsoft Exchange mailbox permissions. Once inside, they pursued accounts holding sensitive shipment information such as train schedules and shipping manifests, and then followed up on other transport companies with business ties to the first victim, exploiting those trust relationships.
The campaign is likely connected to wide-scale targeting of IP cameras in Ukraine and bordering NATO countries. The actors likely used access to private cameras near border crossings, military installations and rail stations to track the movement of materials into Ukraine. The joint advisory that set out the campaign was co-sealed by the Dutch military intelligence service MIVD. [12]
January 1, 2022
16:00 PM
Oil terminal ransomware in ARA ports
2022
On January 29, 2022, a ransomware attack was discovered that had hit oil terminals in ports in the Netherlands, Belgium and the German port of Hamburg. Over the course of 2022, ransomware attacks on oil terminals in Belgium, Germany and the Netherlands forced fuel supplies to be rerouted, and some of these attacks have been linked to the BlackCat and Conti groups, which have ties to state sponsors. [26][14]
January 1, 2021
16:00 PM
Bakker Logistiek ransomware (the 'cheese hack')
2021
In 2021, a ransomware attack on Bakker Logistiek, a provider of conditioned warehousing and transportation, caused a cheese shortage in Dutch supermarkets, notably at Albert Heijn, the largest supermarket chain in the Netherlands. Inside its warehouses, the company no longer knew where products were stored and could no longer plan its transports. The ransomware group behind the attack is unknown. The company speculated that the attackers got in through the Microsoft Exchange ProxyLogon vulnerabilities that had been reported shortly before.
The case became known in the Netherlands as the cheese hack. It shows how a single logistics provider can empty supermarket shelves, and that an organization can be well prepared and still be exposed when one of its supply chain partners is not. [27][28]
Key Trends
for the logistics sector
Logistics is the backbone of the Dutch economy, which also makes it a vulnerable link for cyberattacks. New connected technology is making operations more efficient and the attack surface larger, while geopolitical tension, ransomware and dependence on partners push risk in the same direction. The trends below describe the developments that matter most for logistics in the Netherlands and the EU.
Chain dependencies make every partner a potential way in
Logistics runs on a chain of carriers, distribution centers, service providers and public authorities, and that structure makes companies more exposed to the weaknesses of their partners. An organization can be well prepared and still be badly exposed when one party in its supply chain is not. Across the EU, systems and services are increasingly intertwined, so a disruption at one point ripples through the chain, and threat actors are abusing these cyber dependencies more often to amplify the impact of their attacks.[7][28][2]
In the Netherlands, incidents at suppliers and service providers continue to cause considerable chain damage, and customer data at the affected companies is hit as well, as the Ceva case above shows. Attackers choose this route on purpose: hacking one link can unlock the data or operations of several organizations, and a state-backed campaign has followed up on transport companies with business ties to a first victim, exploiting those trust relationships.[29][8][12]
Geopolitical tension keeps Dutch and European logistics in scope
Logistics has become part of the conflict around Ukraine. The Dutch intelligence services assess that Russian state actors have systematically increased their digital espionage operations in support of military operations since the war began, and Russia-linked hybrid activity in Europe includes attempts to disrupt logistics that support Ukraine. Ports are exposed in a similar way: critical port infrastructure, responsible for 80 percent of global trade, is increasingly under attack by actors tied to Russia, Iran and China, and because most ports are commercially operated yet serve military logistics functions, they are attractive hybrid warfare targets.[30][31][14]
Hacktivists add steady, politically timed pressure. The members of the pro-Russian group NoName057(16) often target logistics companies in NATO member states, and the Netherlands was most recently targeted during the NATO Summit at the end of June. In the 2025 EU picture for transport and ports, nearly 88 percent of incidents were hacktivist-driven DDoS attacks, often timed with political events. The lines between actor types are also blurring: state-aligned intrusions increasingly take on hacktivist characteristics, and hacktivists and cybercriminals use similar tools, so attribution can be murky.[15][25][3][2][4]
Ransomware pressure on transport and logistics is rising
Transport is under sustained pressure across the EU. Between July 2024 and June 2025, 7.5 percent of all EU incidents were directed against transport infrastructure, which placed transport second among sectors. Within transport, logistics is the second most affected subsector after aviation. Hacktivist DDoS attacks are the most frequent, but ransomware remains the most damaging in downtime and costs. Globally, the number of ransomware victims in transportation and logistics rose 25.8 percent quarter on quarter in the first quarter of 2026, from 62 to 78.[3][2][4]
Dutch figures fit this picture. At least 121 unique ransomware incidents were recorded in the Netherlands in 2024, and the members of the Dutch transport association regularly deal with malware and ransomware. In a May 2025 survey, 80 percent of Dutch transport entrepreneurs said cybercrime is a risk to their organization, and 16 percent had suffered financial damage from cyber incidents.[29][11][1]
Connected technology improves efficiency and widens the attack surface
IoT solutions and robotics have raised efficiency and productivity in logistics, but the threat landscape has become more complex along with them. IoT devices that give real-time insight into goods flows, AI systems that support predictive maintenance and cameras that monitor driver alertness all help operations while enlarging the attack surface. The more the sector is connected, the more interfaces have to be secured.[1][7][9]
The risk reaches operational technology too: in 2025 research covering manufacturing, logistics and transportation, and natural resources, more than 12 percent of industrial organizations had OT assets communicating with malicious domains. AI is seen as double-edged in the Dutch transport sector, where 60 percent of entrepreneurs regard AI innovation as a threat to their organization and 55 percent see it as a chance to strengthen cybersecurity.[32][1]
Small IT teams and uneven oversight leave gaps in security
Many transport and logistics companies are small and medium-sized enterprises with small IT departments and infrequent company-wide updates, which means comparably low effort can cause a great deal of damage. In the Netherlands, 53 percent of transport and logistics entrepreneurs see employee discipline as a challenge, against 37 percent across all Dutch business sectors. On spending, 58 percent of survey participants spent about the same on cybersecurity as in 2023, and a minority of 36 percent invested more.[9][1]
Oversight is uneven in Dutch ports as well. As of 2022, only a few of the roughly 3,000 companies in the Port of Rotterdam were designated as vital. The non-vital port companies are not under any form of cyber supervision and have no access to the threat information that the government shares through the National Detection Network.[33]
Criminals use access to logistics systems to reach physical goods
Shipping and logistics companies have become a growing target for cybercriminals because access to their systems can help gangs hijack trucks and containers and get goods into the hands of real-world criminals. A phishing campaign active since September 2025 and aimed at freight and logistics organizations in the US, Germany, France and Lithuania stole more than 1,600 unique credentials from major industry platforms, enabling fraud and cargo diversion.[16][10]
The wider cargo crime picture shows what is at stake, although these figures cover cargo crime in general and not only cyber-enabled cases: in December 2024, 430 new cargo crimes were added to the EMEA theft database, 113 of them with a recorded loss value totaling about €36.9 million.[34]
How to defend yourself
threat model approach
To defend against this threat landscape, it is equally important to gain critical insights into the current resilience level of your organization. To understand thyself it is useful to let (third-party) security specialists assess your defenses and simulate meaningful attacks. When done right, such an approach provides critical insights into the resilience level of the organization against its threat landscape. Hunt & Hackett use its proprietary threat modelling-based approach with its clients in the logistics sector to provide meaningful insights as well as tailored solutions for the strategical, tactical, and operational aspects of their cybersecurity program.
Our approach
Controlling your cybersecurity risks
In their fight against cyber attacks, our customers typically go through several stages of maturity. By ramping up their prevention, detection and incident readiness over time – and optimizing this for their actual threat landscape – they reach a point where they have developed solid resilience against targeted attacks, with only highly controlled and accepted risks remaining.
There is no simple 'fix' to become resilient against the sophisticated cyber threats of today. Without serious resources or processes for systematic security activities, protection against modern cyber threats like ransomware is just a wish. Hunt & Hackett has developed a unique threat- and sector-driven approach to cybersecurity, enabling you to work from your current situation to a highly improved and controlled situation, optimized for your specific threat landscape and context as an organisation.
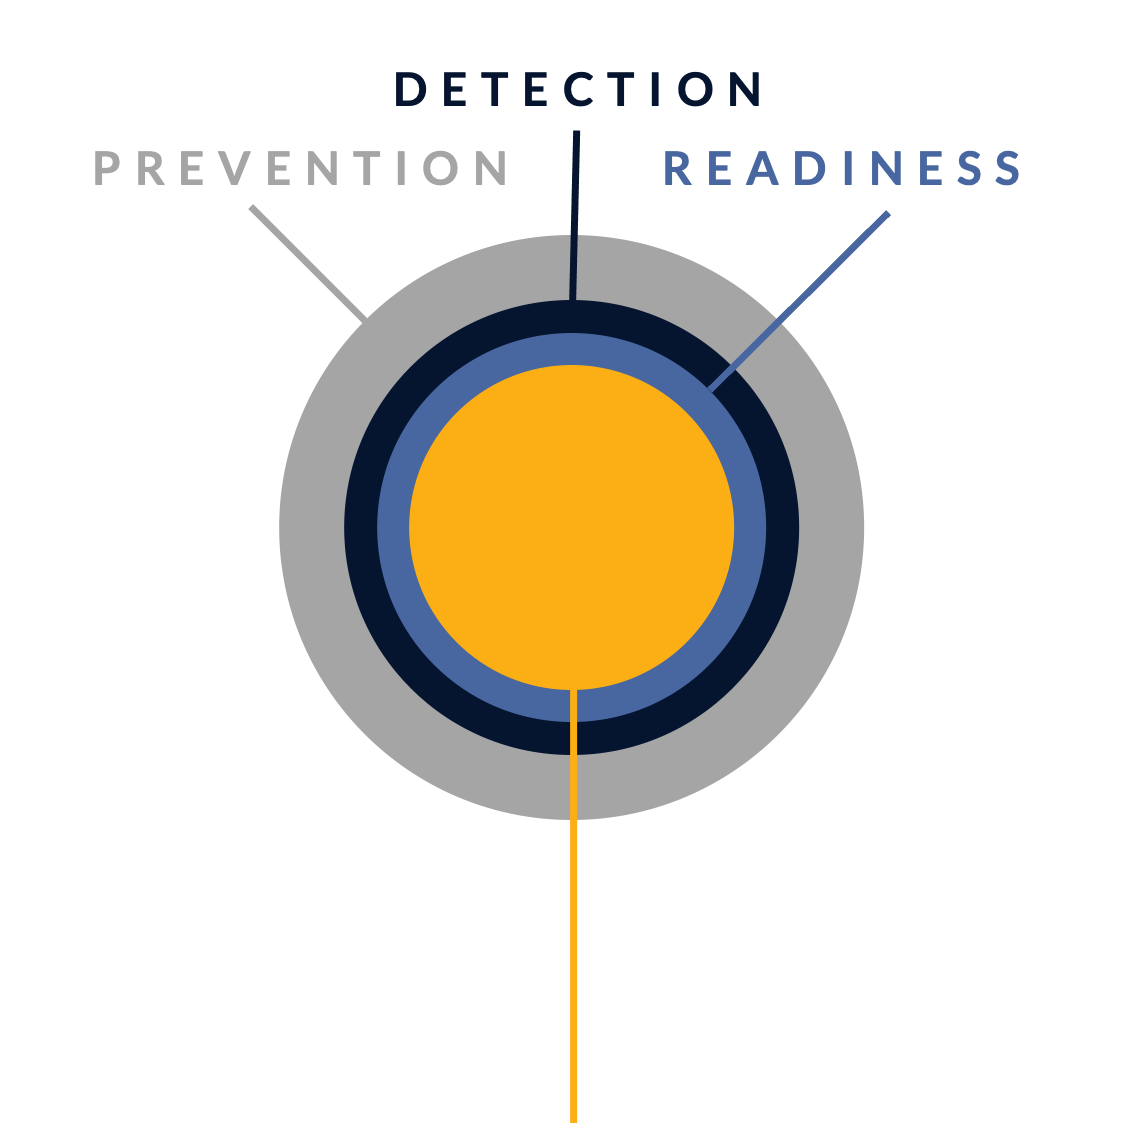
STAGE 1: Unknown risk
Pre-monitoring
-
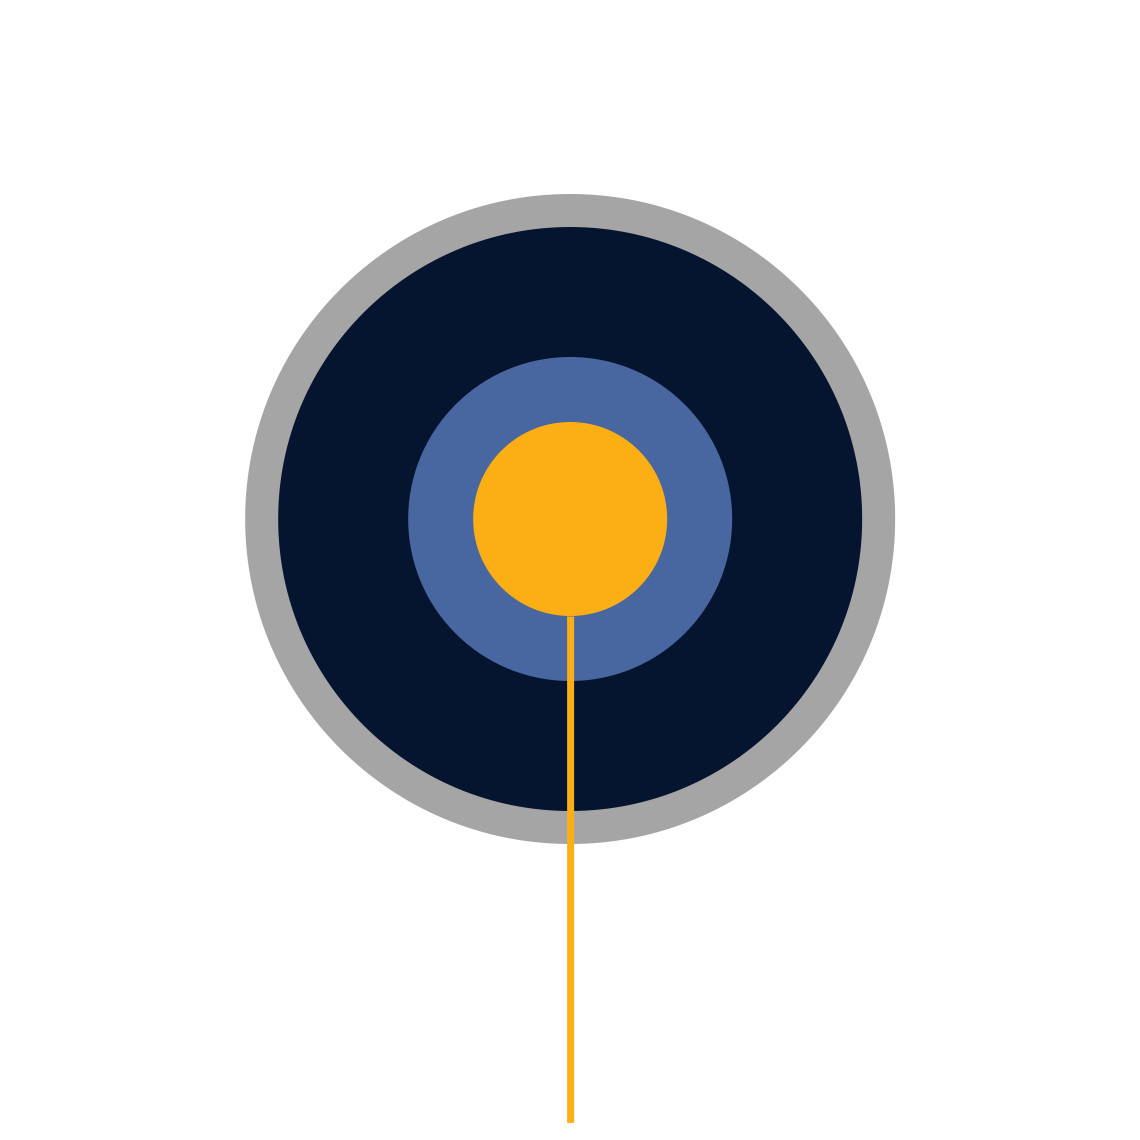
STAGE 2: Reduced risk
Post-monitoring
-
Detection & response controls
Resilience against non-targeted attacks

STAGE 3: Controlled risk
Implemented roadmap
-
Resilience against non-targeted and semi-targeted attacks
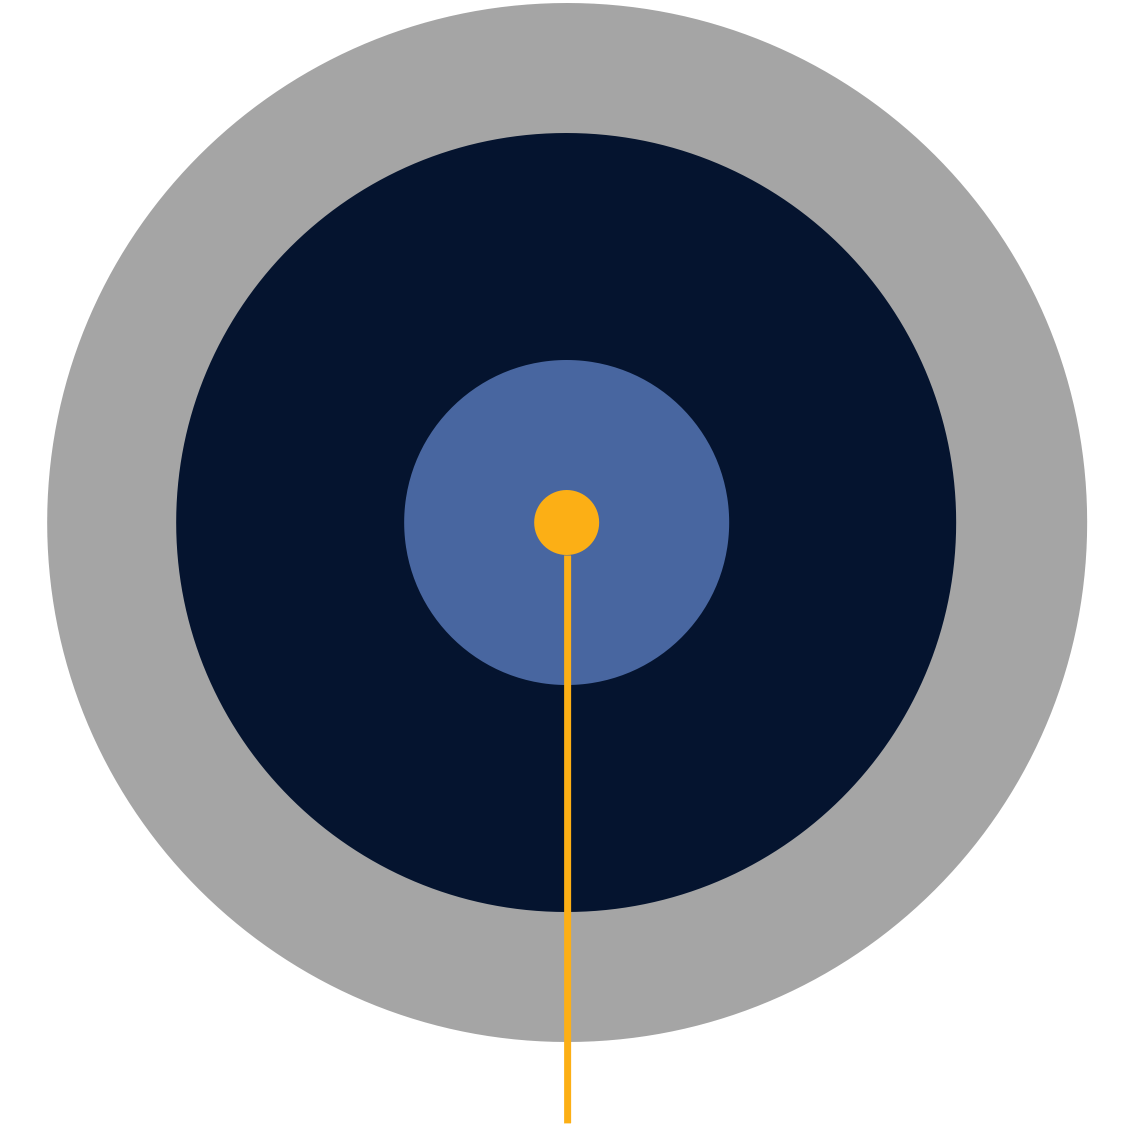
STAGE 4: Highly controlled risk
Targeted attack resilience
-
Our services
Optimized for the logistics sector
Because we use your actual threat landscape and your sector as our starting points, our services are optimised for your specific context and needs.
Managed Detection & Response (MDR)
We detect & react to attacker activity in your environment, minimizing the impact on your business.
Security Program Gap Assessment (SPGA)
We assess your current security program, threat landscape, security controls and risk.
Incident Response (IR)
We help you manage a cyber crisis and contain security incidents, breaches and cyber threats.
Breach & Attack Simulation (BAS)
We validate your security choices by simulating attacks.
Our articles about the logistics sector
From Hunt & Hackett experts
References
[1] ABN AMRO — Transport en logistiek kwetsbare schakel voor cyberaanvallen.
https://www.abnamro.nl/nl/zakelijk/insights/sectoren-en-trends/logistiek/transport-en-logistiek-kwetsbare-schakel-voor-cyberaanvallen.html
[2] ENISA — ENISA Threat Landscape 2025 (press release: EU consistently targeted by diverse yet convergent threat groups).
https://www.enisa.europa.eu/news/etl-2025-eu-consistently-targeted-by-diverse-yet-convergent-threat-groups
[3] FEPORT — ENISA Threat Landscape 2025 highlights cyber risks for transport and ports.
https://feport.eu/news/enisa-threat-landscape-2025-highlights-cyber-risks-for-transport-and-ports-lisbon/
[4] CYFIRMA — Transport & Logistics Q1 2026 Industry Report.
https://www.cyfirma.com/research/transport-logistics-q1-2026-industry-report/
[5] ABN AMRO — Cyberveiligheid in de sector Transport en Logistiek.
https://www.abnamro.nl/nl/zakelijk/insights/sectoren-en-trends/logistiek/cyberveiligheid-in-de-sector-transport-en-logistiek.html
[6] PVO — Cyberaanval in transport: hoe kwetsbaar is jouw bedrijf?
https://pvo-zeelandwestbrabant.nl/nieuws/cyberaanval-transport-hoe-kwetsbaar-is-jouw-bedrijf/
[7] Logistiek.nl — Waarom cybersecurity onmisbaar is in de logistiek.
https://www.logistiek.nl/204124/waarom-cybersecurity-onmisbaar-is-in-de-logistiek
[8] Foley & Lardner — Securing Digital Supply Chains.
https://www.foley.com/insights/publications/2025/11/securing-digital-supply-chains-confronting-cyber-threats-in-logistics-networks/
[9] HHLA — Logistics in the sights of hackers.
https://hhla.de/en/magazine/it-security
[10] CERT-EU — Cyber Brief 26-03 February 2026.
https://cert.europa.eu/publications/threat-intelligence/cb26-03/
[11] NCSC — NCSC - Transport en Logistiek Nederland.
https://www.ncsc.nl/netwerk/transport-en-logistiek-nederland
[12] CISA — Russian GRU Targeting Western Logistics Entities and Technology Companies (joint advisory AA25-141A, co-sealed by MIVD).
https://www.cisa.gov/news-events/cybersecurity-advisories/aa25-141a
[13] NCSC — FERM bundelt krachten Rotterdamse havenbedrijven.
https://www.ncsc.nl/ondernemersverhaal/ferm-bundelt-krachten-rotterdamse-havenbedrijven-tegen-cybercrime
[14] Help Net Security — Ports are getting smarter and more hackable (CCDCOE).
https://www.helpnetsecurity.com/2025/07/23/ccdcoe-maritime-port-cyber-attacks/
[15] NOS — Pro-Russische hackers legden websites Nederlandse havens plat.
https://nos.nl/artikel/2478861-pro-russische-hackers-legden-websites-nederlandse-havens-plat
[16] TechCrunch — Data breach at Ceva Logistics rippling across banks, retailers.
https://techcrunch.com/2026/08/10/a-data-breach-at-shipping-giant-ceva-logistics-is-rippling-across-banks-retailers-steam-gamers-and-beyond/
[17] FreightWaves — Cyberattack on Ceva Logistics warehouses in Europe impacts retailers.
https://www.freightwaves.com/news/cyberattack-on-ceva-logistics-warehouses-in-europe-impacts-retailers
[18] The Record — Cyberattack on logistics giant Ceva hits retailers and Steam customers.
https://therecord.media/ceva-logistics-cyberattack-bol-steam-debijenkorf-ace-tate
[19] Ahold Delhaize — Ahold Delhaize update on status of cybersecurity incident.
https://newsroom.aholddelhaize.com/ahold-delhaize-update-on-status-of-cybersecurity-incident/
[20] IBTimes UK — Albert Heijn deliveries resume after cyber incident.
https://www.ibtimes.co.uk/albert-heijn-deliveries-resume-after-cyber-incident-1826826
[21] NT — Hackers slaan toe bij AB Texel.
https://www.nt.nl/wegvervoer/2024/02/29/hackers-slaan-toe-bij-ab-texel-geen-impact-op-dienstverlening/
[22] The Record — Dutch shipping giant Royal Dirkzwager confirms Play ransomware attack.
https://therecord.media/royal-dirkzwager-ransomware-attack-dutch-shipping
[23] Security Affairs — Play ransomware gang hit Dutch shipping firm Royal Dirkzwager.
https://securityaffairs.com/143714/cyber-crime/play-ransomware-royal-dirkzwager.html
[24] The Record — Pro-Russian hackers claim attacks on French, Dutch websites.
https://therecord.media/prorussian-hackers-claim-attacks
[25] Eurojust — Hacktivist group NoName057(16) taken down.
https://www.eurojust.europa.eu/news/hacktivist-group-responsible-cyberattacks-critical-infrastructure-europe-taken-down
[26] MCAD — EVOS Group hit by ransomware.
https://maritimecybersecurity.nl/incident/N0r68rPzb3
[27] BleepingComputer — Dutch supermarkets run out of cheese after ransomware attack.
https://www.bleepingcomputer.com/news/security/dutch-supermarkets-run-out-of-cheese-after-ransomware-attack/
[28] Crisismanager — NCSC: De grote uitdaging zit in de ketenafhankelijkheid.
https://crisismanager.nl/ncsc-de-grote-uitdaging-zit-hem-in-de-ketenafhankelijkheid
[29] Digital Trust Center — Cybersecuritybeeld 2025.
https://www.digitaltrustcenter.nl/nieuws/cybersecuritybeeld-2025-dreigingen-divers-en-onvoorspelbaar-digitale-basishygiene-op-orde
[30] Security Affairs — Dutch Intelligence Warns Russia Uses Hacked IP Cameras for Military Espionage.
https://securityaffairs.com/195708/intelligence/dutch-intelligence-warns-russia-uses-hacked-ip-cameras-for-military-espionage.html
[31] The Record — Russia stepping up hybrid attacks.
https://therecord.media/russia-cyberattacks-europe-warfare
[32] Claroty — State of CPS Security: OT Exposures 2025.
https://claroty.com/resources/reports/state-of-cps-security-ot-exposures-2025
[33] Computable — Rotterdamse haven slaat alarm over cyberveiligheid.
https://www.computable.nl/2022/08/30/rotterdamse-haven-slaat-alarm-over-cyberveiligheid/
[34] TAPA EMEA — EUR 36.8m stolen from supply chains in EMEA.
https://tapaemea.org/intelligence/e36-8m-of-products-stolen-from-supply-chains-in-emea-in-31-days/