

Cybersecurity for the Technology sector
The technology sector is one of the fastest growing and most influential industries in the world. It continues to expand rapidly, driven by the demand for AI, computing power, electronics, and a wide array of digital services, including Cloud providers, SaaS, PaaS, IaaS platforms and collaboration tools. The sector includes a diverse range of organizations, each contributing to the digital backbone of modern society. Despite their differences, these companies share a common vulnerability: exposure to cyberattacks.
In recent years, Hunt & Hackett has seen a clear increase in activity by Advanced Persistent Threat (APT) groups targeting the technology sector. The combination of cutting-edge innovation and access to sensitive data makes these companies attractive to adversaries focused on espionage, financial gain, or intellectual property theft. And beyond that, tech companies often serve as intermediaries to a large set of underlying organisations or individuals. This makes them attractive targets for supply chain attacks—as seen in cases like the Snowflake (2024), Microsoft Exchange (2021), and SolarWinds (2020) attacks. As these incidents demonstrate, successful attacks on technology firms can have far-reaching and serious consequences.
How can you address this growing threat?
There is this legendary quote from Sun Tzu on how to overcome your adversaries: 'know thy enemy and know yourself; in a hundred battles, you will never be defeated'. To know your enemy starts with gaining an understanding of yourself, your threat landscape, your adversaries’ intentions, their modus operandi, and specific attacking methods. On this page, the cyber threats to the technology sector are explored. Understanding the full picture of the challenges our clients may encounter helps us in doing what we do best: ensuring security for your business from specific cyber threats targeting your organization.
Request a free membership to access our full research insights
Already a member? Login here
Threat landscape
For the technology industry
Advanced Persistent Threats (APTs)
Tactics, Techniques & Procedures (TTPs)
Attack tools
| Technology | Technology + related | All known | |
|---|---|---|---|
| APTs | 439 | 476 | 801 |
| TTPs | 2,907 | 3,378 | 4,112 |
| Attack tools | 2,585 | 2,905 | 3,666 |
Technology faces more cyber threats than ever
To stay in control becomes increasingly difficult
Our proprietary threat diagnostics system shows a significant increase in malicious activity targeting the technology sector. As digital innovation accelerates, so do the risks. The sector continues to attract financially motivated cyber criminals and nation-state actors alike. They are drawn by its access to sensitive data, intellectual property, its strategic role across industries, and by its role as a conduit to other organisations through interconnected supply chains. This, combined with the frequent adoption of new technologies, reliance on third-party providers, and widespread use of cloud services, has significantly expanded the attack surface. High-profile breaches in recent years demonstrate how vulnerabilities can be exploited at scale and how quickly attacks can spiral across interconnected systems. As organizations struggle to keep pace, staying in control becomes more challenging.
The Netherlands shows the pattern clearly. In 2024, the ICT sector was the hardest hit by ransomware, accounting for 24 percent of Dutch incidents, up from 11 percent in 2023. Across Europe, computer systems design and related services account for 5.4 percent of all recorded incidents, the highest rate of any subindustry. Globally, extortion groups named 572 technology organizations on leak sites, far more than any other sector, and initial access brokers advertised access to 277 technology companies, a rise of nearly 30 percent.[1][2][3][4]
This attention has a few causes. First, technology companies are lucrative to extort. Disrupting their operations hurts, and they hold vast stores of monetizable information. Data theft is usually aimed at blackmailing the victim, and if the victim does not pay, the information is published. Second, the sector offers a one-to-many opportunity. Technology providers' systems often connect to multiple customers, so an intrusion at one supplier can interrupt services or open up the rest of a digital supply chain. In the Netherlands, incidents at suppliers and service providers have caused considerable chain damage, with customer data hit as well. Dutch risk analysis rates an attack on a cloud company as both highly likely and high in impact, because an outage or sabotage at one supplier can reach payments, healthcare, energy and government services.[4][5][6][7][8][9]
And third, technology is exactly what states want to acquire. China is actively targeting Dutch researchers, businesses and universities to obtain semiconductor, quantum computing and aerospace technology, and telecommunication firms are priority targets because valuable information can be obtained from them. In 2025, a Chinese espionage campaign reached routers at smaller Dutch hosting and internet service providers. Intellectual property in semiconductor design and manufacturing is a prime target for nations seeking to advance their domestic capabilities quickly. Especially with ASML and NXP based in the Netherlands, the country is embroiled in a chip war between the US and China. Only a limited share of Chinese cyber operations against Dutch interests is probably detected and mitigated.[10][11][12]
Actor overview
The most active attack groups targeting the technology sector are shown in this chart highlighting which motivations are driving the various actors active in this sector.
Knowing the APT groups, their motivations and origin countries provides a solid starting point for understanding what you are up against. To get a more comprehensive understanding of the threat landscape, it is important to research, map, and document your adversaries’ intentions to their modus operandi, attack methods and attack tools, as this provides more actionable information for strenghtening your defences.
More detailed information on the threat landscape for this sector?
Already a member? Login here
How it works
Threat landscape for the technology sector
Attacks in the technology sector
Look down! Look out! Look up!
This section explores several major cyberattacks that have impacted the technology sector in the 21st century. As one of the most frequently targeted industries, tech companies face unique risks due to their broad digital footprint, central role in global infrastructure, and often interconnected services. The incidents highlighted here illustrate just how far-reaching the consequences can be: from regulatory penalties to reputational damage and operational disruption. While these examples offer a window into the threat landscape facing tech firms, they represent only a small subset of the cyber activity taking place across the sector. The true scale of attacks remains vast, often unfolding quietly behind the scenes.
January 1, 2026
16:00 PM
Odido customer-data breach
2026
In 2026, Dutch telecom provider Odido was hit by a major cyberattack in which criminals gained access to a file holding the data of 6.2 million accounts. The data included full names, addresses, phone numbers, customer numbers, email addresses, bank account numbers, dates of birth, and the numbers and expiry dates of identity documents such as passports and driver's licenses. Hunt & Hackett's analysis points to attackers entering a customer relationship management (CRM) environment through phishing and social engineering of two-factor authentication codes, although how the attackers got in has not been officially disclosed.
The method matches one used by the ShinyHunters group, according to a media investigation based on information from the hackers and sources around the breach. A supplier Odido uses to store customer data had repeatedly warned about that same method. The criminals began publishing customer data and threatened to release a million new data points a day for two weeks unless Odido paid a ransom. The remaining stolen data was later published online, covering a total of 6.1 million customers according to Have I Been Pwned. Odido reported the incident to the Dutch Data Protection Authority (AP), which is monitoring whether the company takes the right steps.[13][5][14][15][16]
January 1, 2025
16:00 PM
NoName057(16) DDoS campaign
2025
In April 2025, Dutch payment processor Adyen was hit by three DDoS attacks in one evening. Adyen handles payments for companies such as Meta, Uber, eBay, HelloFresh, and Spotify, and the attacks left its services with "limited availability". People had trouble paying in stores, restaurants, and online. No attribution for the Adyen attacks is given here.
Separately, the Dutch National Cyber Security Center (NCSC) warned that the pro-Russia hacktivist group NoName057(16) was targeting Dutch organizations with large-scale DDoS attacks. One such attack disrupted at least 19 municipal and provincial websites, and an earlier DDoS attack on Logius, the ICT administrator of the Dutch Ministry of Internal Affairs, led to a temporary shutdown of DigiD. The group does not run a traditional botnet. It mobilizes volunteers through Telegram who install the DDoSia client on their own devices. While clearly ideologically aligned with Russia, there is no hard evidence that it is formally part of the Russian state apparatus.[17][18][19]
January 1, 2025
16:00 PM
Citrix NetScaler zero-day exploitation
2025
In 2025, several critical organizations in the Netherlands were successfully attacked through CVE-2025-6543, a vulnerability in Citrix NetScaler. The Dutch NCSC found malicious webshells on the affected Citrix devices, which give an attacker remote access to the system and let them keep that access and carry out further attacks. Hackers exploited flaws in widely used application delivery and remote access systems to breach several critical infrastructure providers, and Dutch authorities warned that the vulnerabilities could affect thousands of systems worldwide.
The NCSC describes the attacks as the work of one or more actors with an advanced way of working: the flaw was abused as a zero-day and traces were actively wiped to hide the compromise. No actor has been named, and considerable uncertainty remains about which organizations were compromised, whether the actor is still active, and what the impact is.[20][21][22]
January 1, 2025
16:00 PM
Chinese state espionage against Dutch technology sector
2017-2025
Chinese espionage against Dutch technology companies has run for years. The Chinese hacker group Chimera had access to the systems of Dutch chipmaker NXP from late 2017. Over the two years it held that access, it focused on obtaining chip designs and on mailboxes holding large amounts of sensitive information. Investigators have also uncovered a remote access trojan developed for FortiGate devices.
More recently, a Chinese cyberespionage campaign tracked as Salt Typhoon and RedMike gained access to routers at smaller Dutch hosting and internet service providers in 2025. Dutch services joined a 13-country advisory in August 2025 attributing that campaign to three Chinese technology companies working on behalf of Beijing. The Dutch military intelligence service MIVD estimates that probably only a limited proportion of Chinese cyber operations against Dutch interests is detected and subsequently mitigated. The Dutch intelligence service AIVD has noted that Dutch companies, knowledge institutions, and the government hold specialized knowledge and technology that cannot be found at that level anywhere else in the world. The case shows that technology companies with unique expertise face patient, long-running espionage, and that much of it may never be detected.[12][10][25]
January 1, 2024
16:00 PM
Nexperia IT breach
2024
In 2024, Nexperia, a Chinese-owned semiconductor company headquartered in the Netherlands, announced it had been hacked after a ransomware group uploaded what it claimed were stolen confidential documents to a darknet extortion site. The Dunghill group, a ransomware gang that began operating in early 2023, claimed the attack. On its leak site, Dunghill said it had stolen 1 TB of data, including trade secrets such as chip designs, employee personal data, and customer information from well-known brands like SpaceX, Apple, and Huawei. As proof, the listing included an employee's passport photo and legal and technical documents. These figures are the attackers' own claims. Nexperia said it disconnected the affected systems from the internet to contain the incident, brought in external specialists to establish its nature and scope, and informed the relevant Dutch authorities, including law enforcement.[23][24]
January 1, 2024
16:00 PM
Snowflake
2024
In mid-2024, Snowflake (a major cloud data warehousing provider) was at the center of a widespread data breach that exposed customer environments across more than 100 organizations in a campaign aimed at data theft and extortion. Mandiant tracks the actor as UNC5537, a financially motivated group suspected of stealing a significant volume of records from customer environments. It assesses with moderate confidence that UNC5537 comprises members based in North America and works with an additional member in Turkey. At least 100 Snowflake customers were confirmed as impacted, and approximately 165 businesses were potentially exposed. The attackers logged in with credentials that were primarily obtained from infostealer malware campaigns on systems not owned by Snowflake. The impacted accounts did not have multi-factor authentication enabled, so a valid username and password was enough to get in.[26][27]
January 1, 2020
16:00 PM
SolarWinds
2020
In 2020, an advanced persistent threat actor began compromising U.S. government agencies, critical infrastructure entities, and private sector organizations, with activity going back to at least March 2020. The attackers added a malicious version of a binary to the SolarWinds software lifecycle, and it was then signed with SolarWinds' legitimate code signing certificate. In April 2021, the U.S. Government attributed the activity to the Russian Foreign Intelligence Service (SVR). CISA judged the threat to pose a grave risk to federal, state, local, tribal, and territorial governments as well as critical infrastructure entities and other private sector organizations.
The damage was amplified by how Orion is used: it typically runs with a significant number of highly privileged accounts, so compromising it can enable further action and privileges in any environment where those accounts are trusted.[28]
Key Trends
For the technology sector
Technology providers sit underneath almost every other sector. Their systems connect to many customers, so a single intrusion can interrupt services or open a path into a wider digital supply chain. In the Netherlands this is sharpened by heavy reliance on a small number of foreign IT suppliers. At the same time, state-backed espionage keeps targeting Dutch technology and know-how, and attackers increasingly get in through identities, edge devices and trusted integrations rather than through the traditional perimeter. The trends below show where the sector is changing and why it matters for security.[6][29]
Dependence on a few foreign cloud providers has become a national-level risk
The Netherlands is increasingly dependent on a limited number of large, mostly American technology companies, so an outage or sabotage at one supplier could affect payments, hospitals, energy supply and government services. In the Dutch national risk analysis, a targeted supply chain attack by a state actor on a large non-European cloud provider is the highest-scoring risk, and its potential impact grows as more software, data storage and IT services move to the cloud. The exposure is already visible: 1,722 websites of Dutch government bodies, semi-governmental bodies or critical companies were found to depend on at least one US-based cloud provider (2025).[9][30][31]
Dependence is now also a matter of policy. Dutch foreign-investment screening increasingly weighs digital sovereignty, data control and operational resilience, as the ban on a US takeover of the cloud company Solvinity shows. One concern is that US laws could allow the American government to block access to DigiD or to request data in secret. At EU level, more than 80% of key digital products, services and infrastructure come from outside the EU, and a 2030 target set in the June 2026 tech sovereignty package aims to cut that to 40%.[32][33][3]
Trusted vendors, SaaS integrations and open-source packages are becoming the preferred route in
Hardware and software reach organizations through a complex chain of suppliers, developers and service providers, so a vulnerability or incident at one party can affect many others. Globally, third-party involvement in breaches jumped 60% year on year and now accounts for nearly half of all breaches, while remediation remains slow. In Europe, computer systems design and related services accounted for 5.4% of all recorded incidents, the highest share of any subindustry, and its share within professional and technical services rose from 27.5% in the first half of 2025 to 38.4% by early 2026.[34][35][3]
Supply chain risk has also moved beyond vulnerable code to the misuse of trusted connectivity: attackers exploit SaaS integrations, vendor tools and application dependencies to bypass perimeters at scale. SaaS application data was relevant to 23% of investigated incident response cases in 2025, up from 6% in 2022. Open-source ecosystems are exposed in the same way, as the compromise of an npm package downloaded 100 million times a week likely exposed millions of downstream users.[36][4]
State-backed espionage against Dutch technology is intensifying and hard to detect
China now probably stands on an equal footing with the United States in offensive cyber capabilities, and it is actively targeting Dutch researchers, businesses and universities for semiconductor, quantum computing and aerospace technology. Espionage against Dutch semiconductor research institutions was described as intensifying, and routers at smaller Dutch hosting and internet service providers were reached in 2025. Dutch military intelligence estimates that probably only a limited proportion of Chinese cyber operations against Dutch interests is detected and mitigated. Globally, more than 58% of state-sponsored targeted intrusions against technology organizations were attributed to China-nexus adversaries, based on observed targeting patterns.[10][37][4]
Attribution is getting harder. State actors expand their cyber programs and use state-backed groups, companies, intermediaries and criminal networks to carry out attacks, and across Europe the same techniques, infrastructure and access mechanisms now appear in cybercrime, hacktivist and state-linked activity. A technology company therefore cannot assume that an intrusion's apparent motive reveals who is behind it.[38][8][39]
Ransomware pressure on the ICT sector keeps rising
In 2024, the ICT sector was the most affected by ransomware in the Netherlands, accounting for 24% of incidents, up from 11% in 2023. That year, 29% of victims paid the criminals. The pattern is global: big game hunting groups named 572 technology organizations on leak sites, far more than any other sector, and initial access brokers advertised access to 277 technology companies, an increase of nearly 30% that points to growing demand for identity-driven access. Worldwide, 7,551 ransomware victims were publicly disclosed between April 2025 and March 2026, a 24.9% increase and the fourth straight year of record disclosures.[2][40][4][41]
Attackers get in through stolen identities and internet-facing edge devices
Two entry routes dominate. Vulnerability exploitation has overtaken stolen credentials as the most common way attackers gain initial access, according to 2026 breach data, yet identity weaknesses still played a material role in almost 90% of incident response investigations in 2025. In Dutch ransomware cases in 2024, the most common entry was account takeover (38%), often with stolen credentials from phishing or cracked passwords, while 33% of attackers exploited vulnerabilities in systems.[35][36][40]
Edge devices are the clearest example of the exploitation route. Almost every organization manages one or more of them and they are reachable from the internet, which makes them an attractive target, a pattern already visible in the successful attacks on Dutch critical organizations through Citrix NetScaler. A further increase in campaigns exploiting vulnerabilities in edge devices such as routers, firewalls and VPN solutions was forecast for 2026.[21][10]
AI speeds up attacks and is becoming a target in its own right
AI compresses the attack lifecycle from access to impact: in 2025, exfiltration speeds for the fastest attacks quadrupled. The Dutch national cybersecurity assessment likewise points to attackers using generative AI to carry out attacks more easily and at greater scale. AI tools are also becoming targets, because they may connect to sensitive files, credentials, browser sessions and development environments, and cybercriminal targeting of common AI assistant ecosystems has been observed.[36][38][6][42]
NIS2 Compliance
For essential and important entities
Since 15 August 2026, the Dutch Cyberbeveiligingswet (Cbw) has been in force, implementing the European NIS2 Directive into national law. The legislation introduces cybersecurity obligations for essential and important entities, including technology companies operating in areas such as digital infrastructure and managed ICT services.
Organisations within its scope must comply with three core obligations: registration, cybersecurity risk management and incident reporting. Key requirements include:
- Risk assessments and appropriate security measures to protect network and information systems
- Incident detection, response and business continuity arrangements
- Supply chain security and vulnerability management
- Policies for assessing the effectiveness of cybersecurity measures
- Management accountability and oversight of cybersecurity risks
- Reporting significant incidents within the legally required timeframes, including an early warning within 24 hours and an incident notification within 72 hours
Hunt & Hackett's Managed Detection and Response (MDR) service supports several of these requirements through continuous security monitoring, threat detection and incident investigation. Our analysts help organisations identify suspicious activity, understand the scope and impact of incidents, and gather the technical information needed to support regulatory reporting.
We have also developed a practical assessment framework that maps NIS2 requirements against established cybersecurity standards, including ISO/IEC 27001:2022, ISO/IEC 27002:2022 and CIS Controls. This helps organisations assess their existing security measures, identify gaps and prioritise improvements in line with their obligations under the Cyberbeveiligingswet.
How to defend yourself
Threat model approach
To defend against this threat landscape, it is equally important to gain critical insights into the current resilience level of your organization. To understand thyself it is useful to let (third-party) security specialists assess your defenses and simulate meaningful attacks. When done right, such an approach provides critical insights into the resilience level of the organization against its threat landscape. Hunt & Hackett use its proprietary threat modelling-based approach with its clients in the technology sector to provide meaningful insights as well as tailored solutions for the strategic, tactical, and operational aspects of their cybersecurity program.
Our approach
Controlling your cybersecurity risks
In their fight against cyber attacks, our customers typically go through several stages of maturity. By ramping up their prevention, detection and incident readiness over time – and optimizing this for their actual threat landscape – they reach a point where they have developed solid resilience against targeted attacks, with only highly controlled and accepted risks remaining.
There is no simple 'fix' to become resilient against the sophisticated cyber threats of today. Without serious resources or processes for systematic security activities, protection against modern cyber threats like ransomware is just a wish. Hunt & Hackett has developed a unique threat- and sector-driven approach to cybersecurity, enabling you to work from your current situation to a highly improved and controlled situation, optimized for your specific threat landscape and context as an organisation.
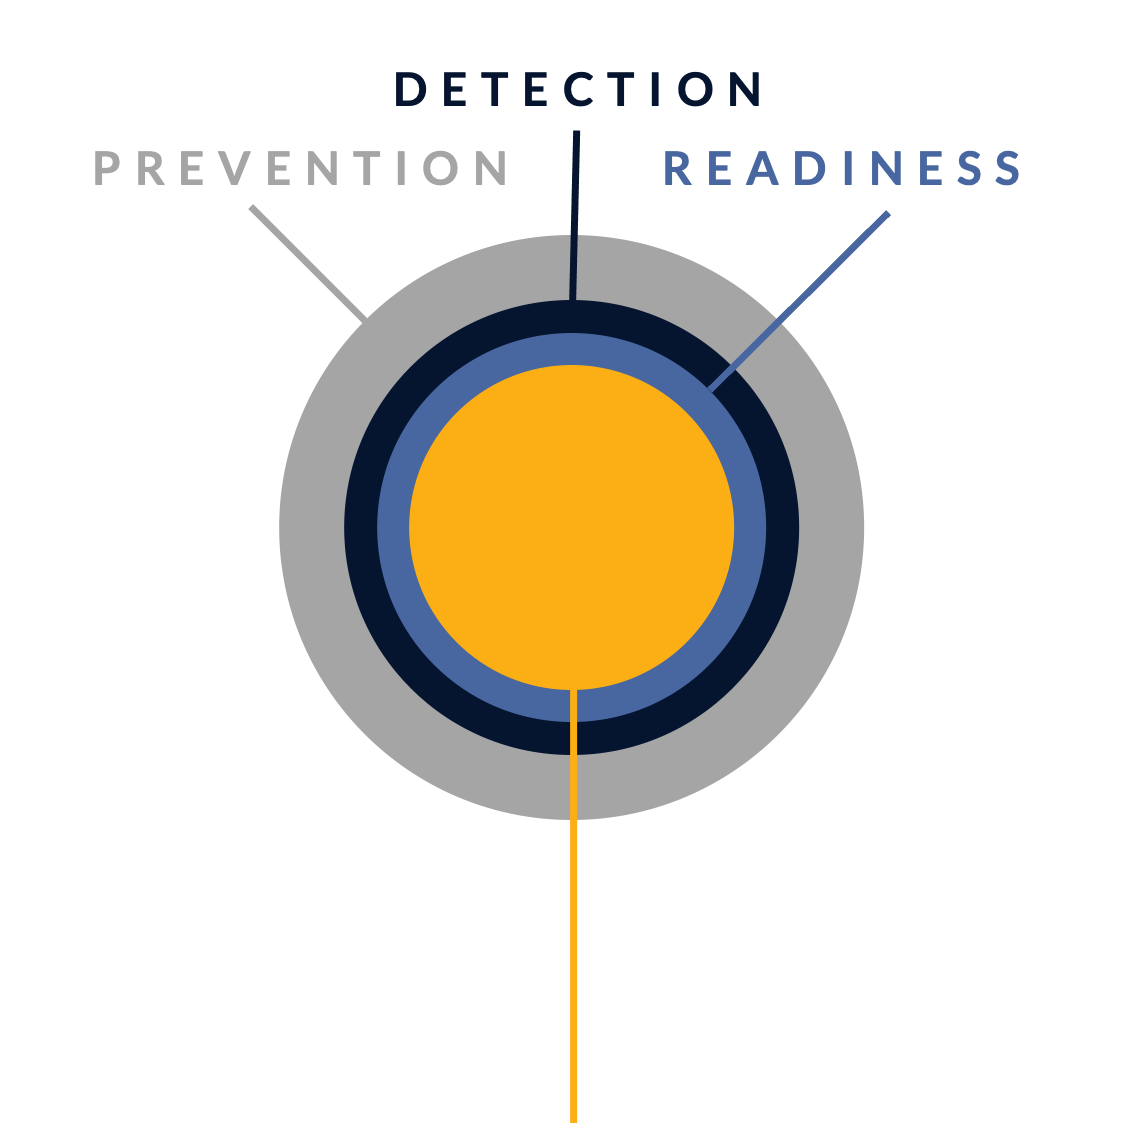
STAGE 1: Unknown risk
Pre-monitoring
-
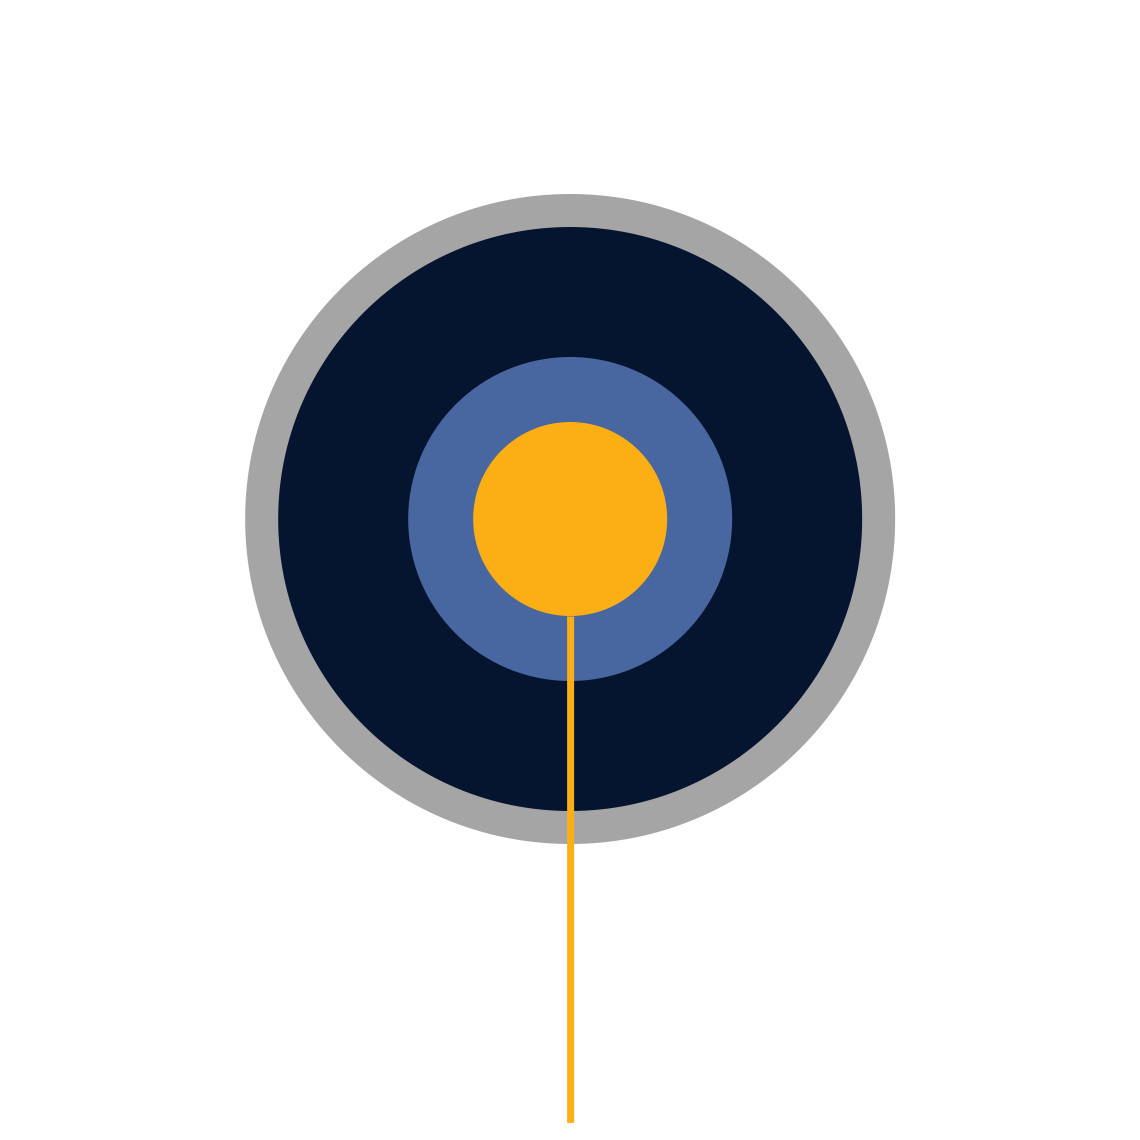
STAGE 2: Reduced risk
Post-monitoring
-
Detection & response controls
Resilience against non-targeted attacks

STAGE 3: Controlled risk
Implemented roadmap
-
Resilience against non-targeted and semi-targeted attacks
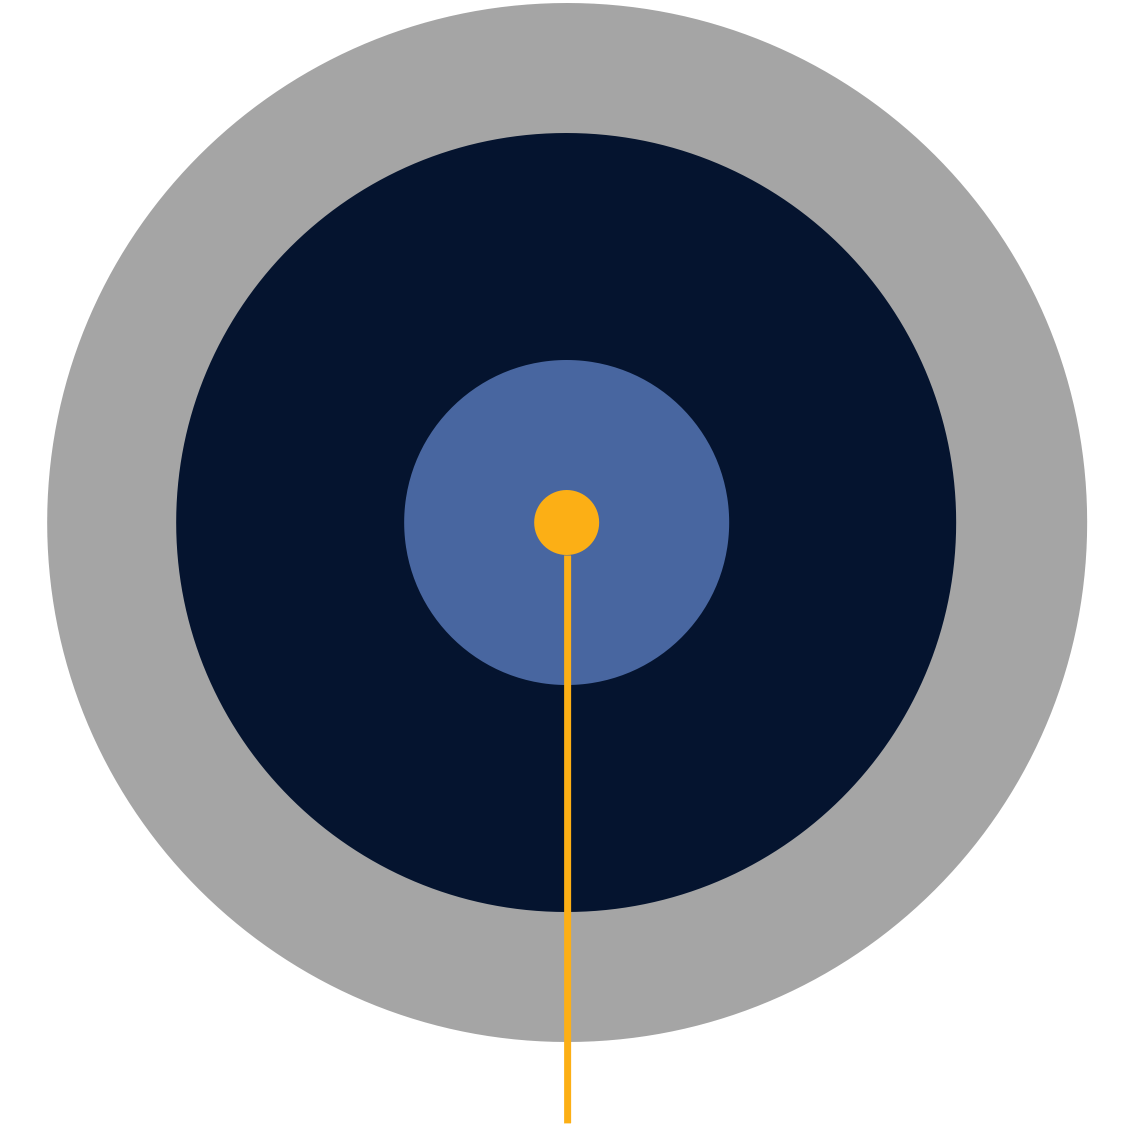
STAGE 4: Highly controlled risk
Targeted attack resilience
-
Our services
Optimized for the technology industry
Because we use your actual threat landscape and your sector as our starting points, our services are optimised for your specific context and needs.
Managed Detection & Response (MDR)
We detect & react to attacker activity in your environment, minimizing the impact on your business.
Security Program Gap Assessment (SPGA)
We assess your current security program, threat landscape, security controls and risk.
Incident Response (IR)
We help you manage a cyber crisis and contain security incidents, breaches and cyber threats.
Breach & Attack Simulation (BAS)
We validate your security choices by simulating attacks.
Our articles about the technology sector
From Hunt & Hackett experts
References
[1] Digitale Overheid — De ICT-sector het zwaarst getroffen door ransomware.
https://www.digitaleoverheid.nl/nieuws/jaarbeeld-ransomware-2024/
[2] Telecompaper — Bijna kwart Nederlandse ransomware-aanvallen treft ICT-sector.
https://www.telecompaper.com/nieuws/bijna-kwart-nederlandse-ransomware-aanvallen-treft-ict-sector--1527892
[3] Black Kite — 2026 European Third-Party Cyber Risk Report.
https://blackkite.com/reports/2026-europe-cyber-risk-report
[4] CrowdStrike — CrowdStrike 2026 Technology Threat Landscape Report.
https://www.crowdstrike.com/en-us/blog/crowdstrike-2026-technology-threat-landscape-report/
[5] Computable — Odido-hack toont: niet de firewall maar de identiteit ligt onder vuur.
https://www.computable.nl/2026/02/17/odido%E2%80%91hack-toont-niet-de-firewall-maar-de-identiteit-ligt-onder-vuur/
[6] Help Net Security — Europe's technology backbone is becoming a cyber target.
https://www.helpnetsecurity.com/2026/09/24/enisa-eu-cyber-threats-report/
[7] NCSC — Cybersecuritybeeld Nederland (CSBN).
https://www.ncsc.nl/producten-en-diensten/cybersecuritybeeld-nederland-csbn
[8] Binnenlands Bestuur — Cyberaanvallen en afhankelijkheid Big Tech bedreigen nationale veiligheid.
https://www.binnenlandsbestuur.nl/digitaal/cyberaanvallen-en-big-tech-bedreigen-nationale-veiligheid
[9] Computable — Cyberaanval op cloudprovider grootste digitale veiligheidsrisico voor Nederland.
https://www.computable.nl/2026/10/19/cyberaanval-op-cloudprovider-grootste-digitale-veiligheidsrisico-voor-nederland/
[10] The Record — China cyber capabilities now equal to the US, warns Dutch intelligence.
https://therecord.media/china-cyber-capabilities-match-us-dutch-intel-says
[11] CSIS — Protecting Our Edge: Trade Secrets and the Global AI Arms Race.
https://www.csis.org/analysis/protecting-our-edge-trade-secrets-and-global-ai-arms-race
[12] TNW — How the Netherlands became a target for cyber espionage.
https://thenextweb.com/news/how-the-netherlands-target-cyber-espionage-europe-worried
[13] NOS — Hack bij Odido, gegevens miljoenen klanten in handen van criminelen.
https://nos.nl/artikel/2602080-hack-bij-odido-gegevens-miljoenen-klanten-in-handen-van-criminelen
[14] Security.NL — Odido waarschuwt miljoenen klanten voor datalek.
https://www.security.nl/posting/924257/Odido+waarschuwt+miljoenen+klanten+voor+datalek+na+hack+klantcontactsysteem
[15] NOS — Toeleverancier Odido waarschuwde voor gebruikte hackmethode.
https://nos.nl/artikel/2604265-toeleverancier-odido-waarschuwde-voor-gebruikte-hackmethode
[16] CCinfo — Cyberaanvallen maart 2026 Nederland en Belgie.
https://www.ccinfo.nl/menu-nieuws-trends/actuele-cyberaanvallen/cyberaanvallen-2026-maart
[17] NL Times — Dutch payment processor Adyen hit by three DDoS attacks.
https://nltimes.nl/2025/04/22/dutch-payment-processor-adyen-hit-three-ddos-attacks
[18] Security Affairs — NoName057(16) targeting Dutch organizations.
https://securityaffairs.com/177312/hacktivism/pro-russia-hacktivist-group-noname05716-is-targeting-dutch-organizations.html
[19] Hunt & Hackett — NoName057(16) hacktivist activities reach the Netherlands.
https://www.huntandhackett.com/blog/noname05716s-hacktivistic-activities-reach-the-netherlands
[20] NCSC — Casus: Citrix kwetsbaarheid.
https://www.ncsc.nl/alerts/casus-citrix-kwetsbaarheid
[21] Security.NL — NCSC treft malware aan op Citrix NetScaler-servers.
https://www.security.nl/posting/897617
[22] CSIS — Significant Cyber Incidents.
https://www.csis.org/programs/strategic-technologies-program/significant-cyber-incidents
[23] The Record — Chinese-owned semiconductor company Nexperia hit by ransomware attack.
https://therecord.media/nexperia-semiconductor-company-ransomware-incident
[24] Infosecurity Magazine — Chipmaker Nexperia confirms cyber-attack.
https://www.infosecurity-magazine.com/news/chipmaker-nexperia-attack/
[25] TU/e Cursor — AIVD continues to warn against knowledge theft.
https://www.cursor.tue.nl/en/news/2026/april/week-4/aivd-continues-to-warn-against-knowledge-theft
[26] Google Cloud / Mandiant — UNC5537 Targets Snowflake Customer Instances.
https://cloud.google.com/blog/topics/threat-intelligence/unc5537-snowflake-data-theft-extortion
[27] Cybersecurity Dive — What we know about the Snowflake customer attacks.
https://www.cybersecuritydive.com/news/snowflake-customer-attacks-what-we-know/719056/
[28] CISA — AA20-352A APT compromise of government agencies (SolarWinds).
https://www.cisa.gov/news-events/cybersecurity-advisories/aa20-352a
[29] NL Times — Netherlands at risk of shutdown from dependence on foreign IT.
https://nltimes.nl/2026/01/28/netherlands-risk-shutdown-dependence-foreign-data-authority-warns
[30] Dutch IT Channel — NCTV: Cyberdreiging en Big Tech-afhankelijkheid bedreigen Nederland.
https://www.dutchitchannel.nl/news/762890/nctv-cyberdreiging-en-big-tech-afhankelijkheid-bedreigen-nederland
[31] NL Times — Reliance on US cloud services by Dutch government greater than thought.
https://nltimes.nl/2025/05/31/reliance-us-cloud-services-dutch-government-greater-previously-thought
[32] Cleary — Dutch Government Blocks Kyndryl's Acquisition of Solvinity.
https://www.clearyantitrustwatch.com/2026/06/dutch-government-blocks-kyndryls-acquisition-of-solvinity-in-first-ever-telecom-fdi-prohibition/
[33] NOS — Staatssecretaris verbiedt Amerikaanse overname Solvinity.
https://nos.nl/artikel/2615885-staatssecretaris-verbiedt-amerikaanse-overname-solvinity-bedrijf-achter-digid
[34] NCSC — Toeleveringsketen (supplychain).
https://www.ncsc.nl/toeleveringsketen
[35] Help Net Security — Verizon DBIR: vulnerability exploitation is dominant initial access vector.
https://www.helpnetsecurity.com/2026/05/20/verizon-2026-dbir-findings/
[36] Palo Alto Networks Unit 42 — 2026 Unit 42 Global Incident Response Report.
https://www.paloaltonetworks.com/resources/research/unit-42-incident-response-report
[37] The Record — Netherlands invokes special powers against Nexperia.
https://therecord.media/netherlands-special-powers-chinese-owned-semiconductor
[38] NCTV — Cybersecuritybeeld 2025 Riskante mix.
https://www.nctv.nl/actueel/nieuws/2025/11/26/cybersecuritybeeld-2025-riskante-mix-in-een-onvoorspelbare-wereld
[39] ENISA — ENISA: how dependencies weaken our digital resilience.
https://www.enisa.europa.eu/news/exploring-the-evolution-of-the-cyber-threat-landscape-how-dependencies-weaken-our-digital-resilience
[40] Dutch IT Leaders — ICT-sector meest getroffen door ransomware in 2024.
https://www.dutchitleaders.nl/news/595063/ict-sector-doelwit-van-bijna-kwart-van-de-ransomwareaanvallen
[41] Black Kite — 2026 Ransomware Report.
https://blackkite.com/reports/2026-ransomware-report
[42] CERT-EU — Cyber Brief 26-03 February 2026.
https://cert.europa.eu/publications/threat-intelligence/cb26-03/